
Cloud security is the set of policies, controls, and technologies that protect data, applications, and infrastructure hosted in cloud environments. As more organizations run workloads on someone else’s servers, keeping that data safe—no matter who owns the underlying hardware—has become one of the core disciplines of modern IT.
Most companies already rely on the cloud for day-to-day operations because it offers agility, flexibility, and scalability that on-premises hardware struggles to match. The tradeoff is that securing resources you don’t physically own works differently from securing a server room down the hall. A strong cloud security program is what makes that tradeoff worth taking.
This guide covers how cloud security works, the main threats, the solutions and tools available, and the practices that keep cloud environments safe.
Key takeaways
- Cloud security protects your data and resources in cloud environments from all kinds of threats.
- Security duties are split between you and your cloud provider in a shared responsibility model.
- Challenges include less direct control and managing security across multiple parties and cloud infrastructure.
- Good cloud security is vital for managing risks, keeping sensitive data private, and meeting regulations.
- Effective cloud security means using encryption, secure configurations, strong access controls continuous monitoring, and a tested incident response plan.
- Understanding your role is key to a strong cloud security setup for your cloud infrastructure.
Cloud security definition
Cloud security is a set of procedures and technologies designed to protect data, applications, and infrastructure, and to defend against external and internal threats. It has become essential as organizations move workloads off-premises to SaaS tools, cloud storage, and hybrid environments, where cloud assets no longer sit behind a corporate firewall. What sets cloud security apart from traditional security is the context it operates in: shared infrastructure, remote access by default, and cloud environments built on resources that scale up and down on demand.
Cloud security vs. traditional security
Traditional security was built for a static world: fixed servers, a defined network perimeter, and users who mostly worked from the office. Cloud security is built for the opposite—resources that move, scale, and are accessed from anywhere. The table below highlights the core differences.
Aspect | Traditional security | Cloud security |
|---|---|---|
Perimeter | Fixed network perimeter defined by physical location | Identity-based; the perimeter follows the user and workload |
Infrastructure | Owned and hosted on-premises | Shared, multi-tenant, and hosted by a cloud provider |
Responsibility | Fully managed by the internal IT team | Shared between the customer and the cloud provider |
Scalability | Limited by hardware; scaling takes time and budget | Elastic; resources scale up or down on demand |
Access model | Assumes users are inside the trusted network | Assumes access from anywhere; verifies every request |
Update cadence | Manual patching and version control | Continuous updates, often automated by the provider |
Visibility | Direct access to hardware and logs | Depends on provider tooling, APIs, and shared logs |
Why is cloud security important?
Cloud environments now hold much of an organization's most valuable data, and the stakes when something goes wrong are measurable in dollars, downtime, and regulatory penalties. Left unaddressed, these risks translate directly into breaches, fines, and lost customer trust—which is why cloud security has moved from an IT concern to a board-level one. Three concrete reasons stand out:
- Protecting sensitive data and containing breach costs. According to IBM’s Cost of a Data Breach Report 2025 the global average cost of a data breach is $4.44 million, and in the US, it reached an all-time high of $10.22 million. Breaches involving data spread across multiple cloud and on-premises environments consistently cost more and take longer to contain. Much of that exposure comes from unauthorized access to cloud assets that were never properly locked down.
- Maintaining compliance and avoiding regulatory fines. GDPR alone can result in fines of up to 4% of global annual revenue and healthcare organizations under HIPAA face some of the highest per-breach costs of any industry. Cloud security controls give organizations the evidence and enforcement they need to meet SOC 2 Type 2, ISO/IEC 27001:2022, HIPAA, PCI DSS, and similar frameworks.
- Supporting digital transformation and avoiding costly downtime. As companies move more workloads to SaaS, IaaS, and hybrid setups, an outage or misconfiguration can freeze operations. Industry estimates put the average cost of unplanned downtime at roughly $5,600 per minute across organizations, and 41% of mid-to-large enterprises report hourly downtime costs of $1 million or more. Strong cloud security reduces the likelihood—and blast radius—of these events.
How does cloud security work?
Cloud security helps organizations by providing various controls to protect against threats to data, applications, and cloud systems. As cloud computing platforms are a go-to solution for most businesses, the threats targeting businesses are frequently directed at the cloud. Incorporating the shared responsibility model, cloud security mandates a collaborative effort between the cloud service provider (CSP) and the customer:
- CSP's responsibility: secure the underlying cloud infrastructure—compute, storage, and networking hardware—and the platforms built on top.
- Customer's responsibility: secure data and applications "in" the cloud, including access controls, identity management, and data encryption.
Therefore, cloud security solutions help businesses in several ways:
- Increase transparency. Clear responsibilities make it easier for both sides to secure what they own.
- Monitor network activity. Continuous visibility into traffic and configuration changes catches risks early.
- Add security layers Provider and customer controls work together to protect sensitive information against unauthorized access.
- Strengthen identity management Defined roles make access policies easier to enforce.
- Align to compliance A clear split of duties supports evidence collection for audits.
This shared responsibility model is the foundation of a resilient cloud security strategy—a well-defined division of tasks that keeps both sides accountable.
Types of cloud service models
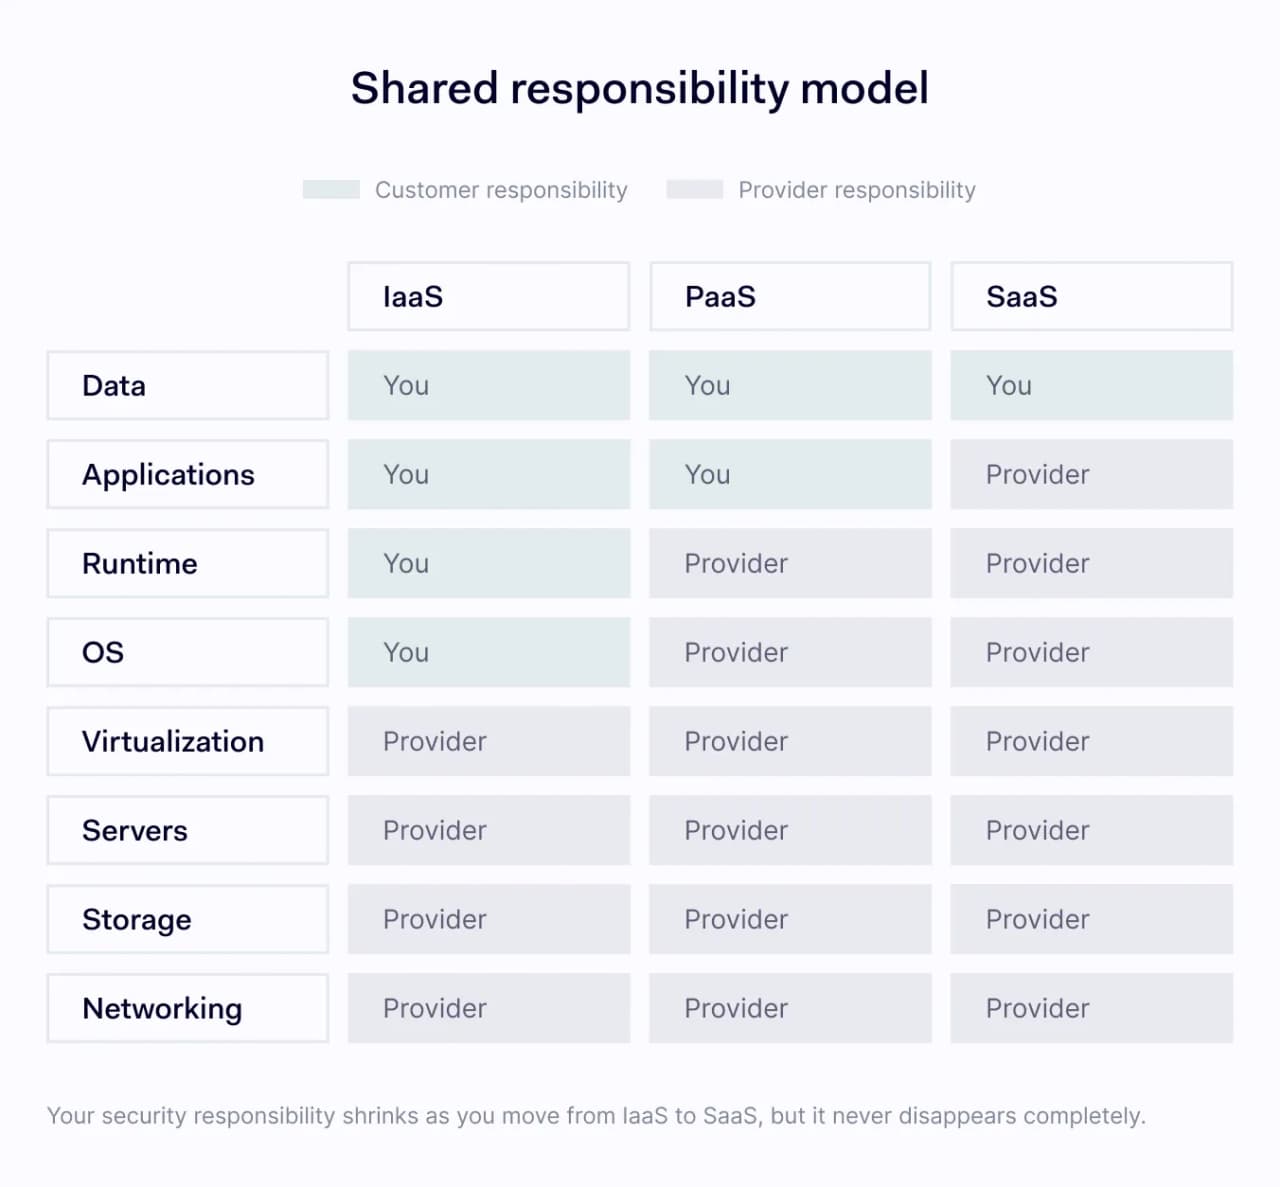
Cloud computing can be delivered as three distinct service models, each providing a unique set of benefits that could serve various business needs.
IaaS
Infrastructure as a Service delivers virtualized data-center resources: compute, storage, and networking. From a security standpoint, IaaS gives you the most flexibility and the most responsibility. You configure the operating system, network rules, patching, and access controls, so misconfigurations and unpatched systems are the biggest risks to watch.
PaaS
Platform as a Service provides a development environment with built-in design, testing, and deployment tools, so teams can ship applications faster. Security responsibility is shared more evenly here: the provider secures the runtime and OS, but you're on the hook for application security, secure coding practices, API protection, and how identities interact with your apps.
SaaS
Software as a Service delivers applications over the internet, usually on a subscription. The vendor controls the full stack while users interact with the software from their endpoint. Your security work shifts to identity, access, and data: enforcing SSO and MFA, controlling who can see what, preventing data leakage, and monitoring for shadow-IT use of unsanctioned SaaS apps.
Types of cloud environments
Cloud computing can be set up in more than one way, and even similar setups can look different across organizations. Each type has strengths and weaknesses that affect security and cost.
Public clouds
A public cloud is an environment distributed on demand over the public internet by a service provider. Some public clouds are free for everyone, while others require a subscription or are priced under pay-per-usage models. The largest public cloud providers include Google Cloud, Amazon Web Services, Microsoft Azure, and IBM Cloud.
Such services help forward-thinking businesses move their workloads externally and easily scale up or down according to their needs. This frees up on-premise network administrators and helps to drive IT costs down. It's much cheaper to use a shared infrastructure managed by a third party than to have the same setup scale in-house.
Private clouds
A private cloud is a cloud environment in which all hardware and software resources are reserved and accessible to a single customer. Often, these environments are protected behind the group's firewall. This creates completely isolated access with no overlaps with other cloud users.
Most companies prefer private cloud setups as it's a much easier way to ensure security and meet compliance requirements. However, one major flaw of this setup is that it isn't as scalable as a public cloud. Private clouds usually are fixed size and can't be upscaled or downscaled at a moment's notice. Additional hardware and software licenses would be necessary to upscale a private cloud.
Hybrid clouds
A hybrid cloud is an environment in which applications run from different sources: cloud and on-premises. This method is the most prominent cloud computing setup, as most businesses get the best of both worlds. Most businesses are using the infrastructure they have built for a long time and expanding it with cloud additions.
Connecting cloud and on-premises environments are usually done with local area networks (LANs), wide area networks (WANs), virtual private networks (VPNs) and other methods. The whole setup is managed from an integrated management and orchestration platform.
Multi-clouds
Multi-clouds are combinations of different cloud types, public or private. This setup is created when different clouds (often from different service providers) are combined by some method of integration or orchestration. This helps to avoid vendor lock-in and create more flexible solutions adapted to specific business needs.
Frequently, such setups are created for one cloud to function as a backup in case of data loss prevention. If some accidents happen, the organization’s data could be safely recovered from the backup.
Cloud security threats
Cloud computing introduces specific security risks that traditional environments don't face in the same way. The main ones to plan for:
- Control challenges. Cloud services extend beyond traditional corporate boundaries, complicating the management of security protocols and reducing direct oversight.
- Multitenancy concerns. In a shared cloud-based infrastructure, a security breach in one tenant's environment can potentially compromise the security of others, illustrating the interconnected risks of cloud computing.
- Shadow IT risks. The proliferation of unauthorized IT setups, especially with BYOD policies, creates vulnerabilities as these setups often bypass official security measures, opening avenues for data exposure.
- Credential theft and DDoS threats. They show the need for strong access controls and proactive measures to mitigate overwhelming traffic that can disable services.
- Ransomware and external breaches. Such attacks endanger data integrity and highlight the crucial shared responsibility between providers and clients in cloud security.
- Weak authentication and API vulnerabilities. Insufficient authentication methods and API insecurities jeopardize sensitive data security.
- Misconfigurations. Misconfigured storage buckets, permissive IAM roles, and open ports remain one of the leading causes of cloud data exposure: even a single default setting left unchanged can expose entire datasets to the public internet.
- Insecure APIs. Cloud services are built on APIs, and any that lack proper authentication, rate limiting, or input validation can be abused to exfiltrate data or pivot deeper into the environment.
Cloud security calls for constant attention. Tightening configurations, enforcing strong authentication, and securing API access are essential steps against the range of threats cloud environments face.
Main benefits of cloud security
Cloud security benefits organizations in several ways:
- Prevents cyber attacks. Cloud security acts as a shield against hackers, thwarting potential attacks before they cause harm.
- Improves data security. Advanced encryption and threat detection safeguard sensitive information from unauthorized access.
- Facilitates cloud maintenance. Continuous monitoring and support by cloud providers strengthens the reliability of cloud services.
- Speeds up recovery. Enables quicker organization and execution of recovery strategies following a data breach, reducing downtime.
- Supports compliance. Helps meet SOC 2 Type 2, ISO/IEC 27001:2022, HIPAA, PCI DSS, and other compliance requirements.
- Streamlines access management. Precisely controls user access rights and monitors activity to swiftly identify and mitigate threats
- Centralizes security controls. Simplifies management of security measures, reducing the risk of errors and boosting operational efficiency.
- Improves visibility and control. Provides comprehensive oversight across cloud environments, improving response to security incidents.
- Adapts to your needs. Allows organizations to tailor security settings to their specific needs, enhancing protection.
- Scales with the business. Security measures can be adjusted as organizational needs evolve, ensuring continued protection against new threats.
- Deploys quickly. Cloud-based security solutions can be rapidly deployed, swiftly extending protection to new business areas.
- Lowers costs. Reduces the need for extensive on-premise security infrastructure, lowering overall IT security expenditures.
- Enables faster threat detection and response. Centralized logging, automated alerting, and integrated playbooks help teams spot and contain incidents before they spread across the environment.
Types of cloud security solutions
Cloud security is not a single product—it’s a stack of specialized solutions and tools, each handling a specific part of the problem. From identity and access management to workload protection, the eight most common categories are:
Identity and access management (IAM)
Identity and access management (IAM) combines frameworks and technologies that manage digital identities and control who can access which resources. IT teams can use IAM to control how an organization's resources are accessed, preventing unauthorized access by issuing each user a unique identity that can be monitored, restricted, and revoked centrally.
Data loss prevention (DLP)
Data loss prevention (DLP) is a set of tools and processes used to ensure the safety of business data. It uses various tools like data encryption, preventative measures, and remediation alerts to protect the data in transit or at rest.
Security information and event management (SIEM)
Security information and event management (SIEM) is a security management approach to orchestrate an organization's IT security. It uses various information and event management tools to create a single dashboard using AI to correlate data across multiple platforms. This allows one to easily have a full panoramic view of the organization's security.
Business continuity and disaster recovery
Business continuity (BC) and disaster recovery (DR) tools provide organizations with tools, services, and protocols to restore an organization after an accident. These services help organizations to reduce the risk of data loss and reputational harm and improve ongoing business operations.
Cloud workload protection platform (CWPP)
A security layer designed to protect workloads—VMs, containers, and serverless functions—as they move across cloud environments. CWPPs handle vulnerability management, runtime protection, and system hardening.
Cloud access security broker (CASB)
A control point between cloud users and cloud services that enforces security policies across SaaS and IaaS. CASBs give visibility into shadow IT, apply DLP, and control how sanctioned apps are used.
Cloud security posture management (CSPM)
A set of tools that continuously monitor cloud configurations to detect misconfigurations, policy drift, and compliance gaps. CSPM is one of the most direct answers to misconfiguration risk.
Cloud-native application protection platform (CNAPP)
A newer category that combines CWPP, CSPM, and other cloud-native controls into one platform. CNAPP is designed to secure applications from development through runtime, giving teams a single view across code, workloads, and configurations.
Compliance and regulatory considerations
Any organization handling sensitive data in the cloud has to plan for compliance, not just security. The frameworks that come up most often:
- GDPR (EU). Governs the personal data of EU residents. Requires lawful processing, data minimization, breach notification within 72 hours, and can impose fines of up to 4% of global annual revenue.
- HIPAA (US healthcare). Sets rules for protecting ePHI, including access controls, audit logs, and breach reporting.
- PCI DSS. Applies to organizations handling payment card data; requires encryption, network segmentation, and strict access controls.
- SOC 2 Type 2. Evaluates how well an organization's controls protect customer data over time across security, availability, confidentiality, processing integrity, and privacy.
- ISO/IEC 27001:2022. The leading international standard for information security management systems.
- NIS2 (EU). Expands cybersecurity obligations for essential and important entities, including incident reporting and supply-chain security.
Cloud security tooling helps meet these requirements in practical ways: identity and access management enforces least-privilege access, CSPM proves configurations stay within policy, SIEM produces the audit logs regulators expect and supports ongoing threat detection, and DLP shows sensitive data is being protected in transit and at rest.
Compliance is never guaranteed by tooling alone, but the right stack makes audits far less painful.
How to secure the cloud
These practices form the working core of any cloud security program and directly reduce the most common security risks in cloud environments.
- Encrypt data in transit and at rest. Encryption protects information while it moves between systems and while it's stored, so a breached server does not automatically mean exposed cloud assets.
- Harden configurations. Change default passwords, close unused ports, apply provider-recommended baselines, and review permissions on storage buckets and databases regularly.
- Enforce strong authentication and MFA. Passwords alone are not enough. Multi-factor authentication should be required for all users, and privileged accounts should use phishing-resistant methods such as hardware keys to block unauthorized access even if credentials leak.
- Apply least-privilege access. Grant users and services only the permissions they need for the task at hand, and review those permissions on a set schedule. Over-permissioned accounts are one of the most common paths attackers use to move laterally.
- Monitor continuously. Feed logs from your cloud provider, workloads, and identity systems into a SIEM or equivalent, and set alerts for unusual activity. Continuous monitoring turns cloud visibility from a snapshot into a live feed and shortens the window for threat detection.
- Keep patching and vulnerability management current. Cloud providers patch the underlying infrastructure, but you're responsible for your workloads, containers, and dependencies. Automate patching wherever possible and track known vulnerabilities against your inventory.
- Plan for incidents before they happen. Build and test an incident response plan that covers detection, containment, eradication, recovery, and communication. Run tabletop exercises so the plan is muscle memory, not a document nobody has read.
- Review your contract with the provider. A clear division of responsibilities helps close the gray zones attackers exploit and makes it easier to see where your side of the shared responsibility model needs strengthening.
The role of zero trust in securing your cloud
While all the above are important cloud security practices, organizations must adopt a comprehensive, architecture-level approach to safeguard their critical cloud resources and data. A zero-trust framework shifts the focus from network perimeters to individual access. Under this principle, all users and devices are considered untrusted by default, and every access request is verified through strong authentication before being granted only the necessary privileges.
This prevents lateral movement of attackers while stopping both external and internal threats in their tracks. Implementing zero-trust solutions ensures continuous validation and inspection of all cloud components, users, and transactions—and it pairs naturally with modern threat detection and response tooling, so any anomaly is investigated in real time. By automating ongoing verification across all entities and interactions, zero-trust tools are integral to securing cloud environments.
Finally, for organizations relying on third-party providers, it's hard to overstate how important it is to review the terms of service. A clear division of responsibilities helps close the gray zones that attackers exploit and makes it easier to see where your setup needs strengthening.