
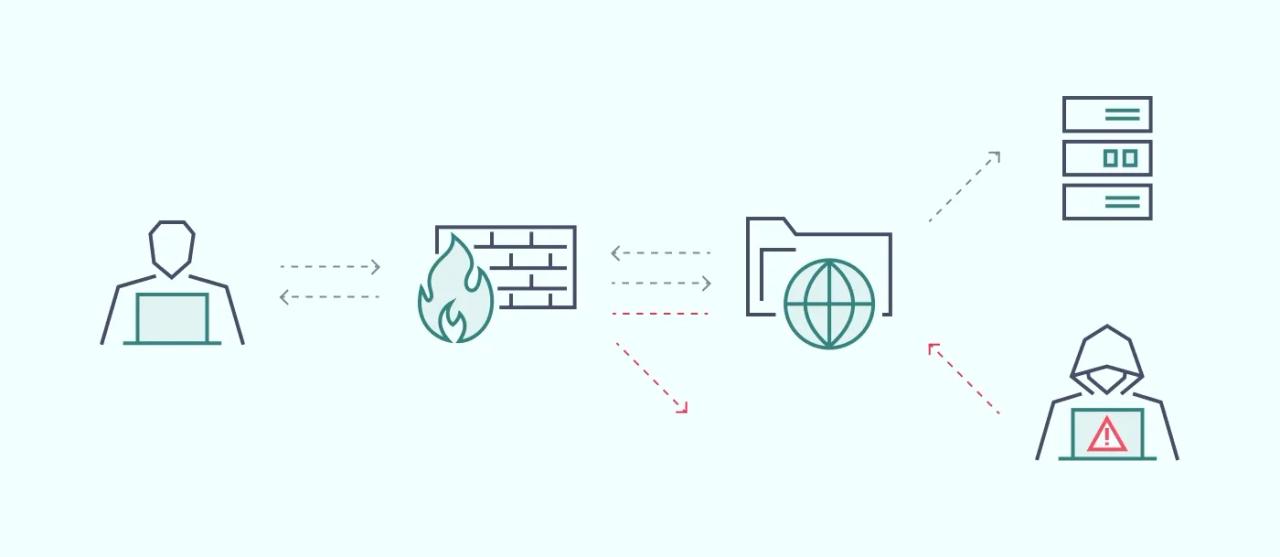
A firewall is a network security system that monitors incoming and outgoing traffic and decides what to allow or block based on a defined set of rules. It is a control placed between networks, systems, or security zones—such as a trusted internal network and the public internet, two internal segments, or an individual device and everything around it—to filter traffic according to those rules Firewalls can be delivered as hardware appliances, software installed on a device, or cloud-based services.
Your network can be compared to an office building with multiple entrances. A firewall is like the security team at every door, checking credentials against a rulebook and turning away anyone who does not belong.
Key takeaways
- A firewall is a network security control that filters traffic between trusted and untrusted networks based on predefined rules.
- Firewalls defend against external threats and limit the damage caused by insider threats through traffic inspection, network segmentation, and activity logging.
- There are 3 levels of inspection: packet headers, connection state, and payload contents.
- Types of firewalls include packet filtering, stateless, stateful, proxy, circuit-level, WAF, NGFW, UTM, and virtual firewalls, with AI capabilities and hybrid mesh architectures layered on top.
- Delivery options—hardware, software, and cloud—should match the organization’s size, infrastructure, and compliance needs.
- Firewalls are not a replacement for antivirus or a VPN; the 3 work together as layered defenses.
What does a firewall do?
A firewall is a computer security system that monitors and controls traffic filtering. The software or hardware unit selectively blocks malicious traffic or allows data packets to pass through according to established security rules.
What is the primary function of a firewall? To enforce your traffic policy at the network boundary, allowing legitimate connections and blocking everything else. In practice, this breaks down into 4 core jobs:
- Filtering inbound traffic. Blocking unauthorized connections, exploits, and malware delivery attempts from the public internet before they reach internal systems.
- Controlling outbound traffic. Preventing compromised devices from reaching command-and-control servers, and limiting data exfiltration by denying unsanctioned destinations.
- Network segmentation. Separating the network into zones (for example, guest Wi-Fi, finance, production servers) so that a breach in one segment does not spread laterally.
- Logging and auditing. Recording connection metadata—source, destination, port, protocol, allow/deny decision—for incident investigation, policy tuning, and compliance evidence.
Firewalls address two distinct categories of risk. External threats include scanning, brute force attempts, exploit traffic, and malware delivery from the internet. Insider threats come from people with legitimate access (employees or contractors who misuse that access, whether on purpose or by accident) and often show up as lateral movement or data being sent somewhere it shouldn’t go. Compromised endpoints sit between the two categories: a device taken over by malware or an outside attacker, acting from inside the network. A well-configured firewall limits all of these threats.
Many firewalls also apply DNS-based filtering to block known malicious domains, enforce acceptable use policies, and deny access to specific URL categories or IP ranges, all without inspecting the full payload.
How does a firewall work
A firewall intercepts traffic in its path and evaluates each packet or connection against a rule set. The decision is binary—to allow or deny—but the data the firewall uses to make that decision can be either shallow or deep. Modern firewalls inspect traffic at 3 progressive depths:
- Packet headers. The firewall reads the source and destination IP addresses, port numbers, and protocol. This information is enough for a packet filtering firewall to make a decision.
- Connection state. The firewall tracks whether a packet belongs to an established, legitimate session. Stateful firewalls use this context to block out-of-sequence or unsolicited packets.
- Payload (deep packet inspection (DPI). The firewall opens the data portion of the packet to look for malware signatures, application-specific commands, or policy violations. Next-generation firewalls (NGFWs) and web application firewalls (WAFs) operate at this level.
Back to the office building analogy: a header check is the guard glancing at your badge, a state check is the guard remembering they just let you out 5 minutes ago, and deep packet inspection is the guard opening your bag. A single packet’s journey through a modern firewall typically looks like this:
- The packet arrives at the firewall interface.
- The firewall reads the header: who sent it, where it is going, and which port and protocol it uses.
- It checks the connection state table to see if the packet belongs to an existing session.
- If deep inspection is enabled, the firewall decrypts the packet (where allowed), reconstructs the payload, and scans it for cyber threats or policy matches.
- The rule engine applies the first matching rule, which may result in forwarding, dropping, or rejecting the packet with a response.
- The decision and metadata are written to the log.
For example, a packet from an unrecognized external IP targeting a closed internal port is dropped at step 2. A packet carrying a known exploit signature inside an allowed HTTPS session is dropped at step 4.
Types of firewalls
Firewalls can be categorized in two ways: by how they inspect traffic and by how they are delivered The inspection method determines what the firewall can see and block, from basic header checks to full payload analysis. The delivery method determines where the firewall runs and how it scales—on a dedicated appliance at the edge, as software on a single device, or as a cloud service that follows your users wherever they work
By method of operation
Packet filtering firewall
A packet filtering firewall is one of the earliest types of firewalls, operating at the network layer. It inspects each packet’s header—source and destination IP, port, protocol—and allows or blocks traffic based on static rules Fast and lightweight, but blind to connection context and payload content, which leaves it exposed to spoofing, fragmented-packet attacks, and payload-based malware. Still common in low-risk perimeter roles and inside routers.
Stateless firewall
A stateless firewall evaluates each packet in isolation, using only the information in its header. It keeps no record of previous packets, which makes it fast and simple to configure but unable to detect attacks that depend on connection context, such as session hijacking or out-of-order packet injection. Stateless firewalls are typically used where performance matters more than inspection depth for example, in high-throughput edge filtering.
Stateful inspection firewall
Stateful firewalls track active connections in a state table and evaluate each packet against the context of its session. Operating at the network and transport layers, they allow return traffic for legitimate outbound connections and block unsolicited inbound packets Context-aware filtering makes them more accurate than stateless alternatives, but they can still be vulnerable to man-in-the-middle (MitM) and denial-of-service (DoS) attacks that abuse the connection state itself.
Circuit-level gateway
Circuit-level gateways work at the session layer and monitor TCP handshakes to confirm a session is legitimate before allowing traffic to flow. They do not inspect packet contents, which keeps them fast but limits them to session-level decisions. They are typically deployed in front of more thorough firewalls as a first-pass filter
Proxy firewall (application-level gateway)
A proxy firewall sits between the client and the destination server, terminating the client connection and opening a new one on the client’s behalf. All application-layer traffic is inspected before it is forwarded. This removes any direct connection between the two endpoints and enforces policy at the application level. However, the trade-off is latency: a single proxy serving many users can become a bottleneck.
Web application firewall (WAF)
A WAF protects web applications by filtering and monitoring HTTP and HTTPS traffic. It defends against application-layer attacks, such as SQL injection, cross-site scripting (XSS), cross-site request forgery, and file inclusion exploits. When deployed in front of a web application as a hardware, software, or cloud-based service, a WAF can update its rules more quickly than most other types of firewalls, enabling it to react swiftly to new attack patterns.
Next-generation firewall (NGFW)
An NGFW combines stateful inspection with application awareness, identity awareness, deep packet inspection, and integrated intrusion prevention. NGFWs can enforce rules based on users and applications, not just IP addresses and ports. They can also inspect encrypted traffic where decryption is permitted. Most NGFWs also include sandboxing, which executes suspicious files in an isolated environment before letting them through. This makes NGFWs the default choice for mid-market and enterprise perimeters.
Unified threat management (UTM) firewall
A UTM firewall bundles firewall, intrusion detection and prevention antivirus, VPN, and content filtering into a single appliance or service. The appeal is operational simplicity: one console, one vendor, one license. UTM is a strong fit for small and medium-sized organizations that need layered protection without a dedicated security team though consolidating many functions in one device can affect throughput under heavy load.
Virtual firewall
A virtual firewall is deployed as software inside a virtualized or cloud environment to protect virtual machines, containers, and east-west traffic between workloads. It scales with the environment it protects and integrates with cloud-native controls VPN gateways and intrusion prevention systems. Virtual firewalls are standard in public and private cloud and hybrid architectures, which traditional hardware appliances cannot reach.
AI-powered firewalls
AI-powered technology is a capability layer rather than a firewall category of its own. The same machine-learning techniques appear in NGFWs, WAFs, cloud firewalls, and virtual firewalls. These models can classify unknown traffic, detect anomalies in connection patterns, and identify potential false positives for review. This reduces the manual tuning required to keep rule sets current. Expect to see AI capabilities packaged as part of a product you already recognize, not as a standalone firewall type.
Hybrid mesh firewalls
Hybrid mesh is an architecture, not a product category. Gartner formalized the term in its first Magic Quadrant for the segment in August 2025. The model unifies firewall management and enforcement across hardware appliances, virtual firewalls, and cloud firewall instances through a single control plane, so policy stays consistent across data centers, branch offices, and multiple clouds. This architecture is intended for organizations whose traffic no longer flows through a single perimeter.
By delivery method
Hardware firewalls
Self-contained appliances that sit at the network edge and enforce policy for every device behind them. Because they are dedicated hardware, they do not consume host resources and can handle high throughput Hardware firewalls suit medium and large organizations with a defined network perimeter but require physical deployment, maintenance, and skilled configuration.
Software firewalls
A software firewall runs on a specific host, such as a laptop, server, or workstation, and protects that device. It inspects traffic entering and leaving the device which is useful for defending endpoints that leave the corporate network. The trade-off is that each device uses some of its own CPU and memory to run the firewall.
Cloud firewalls
Cloud firewalls (FWaaS) are hosted and delivered by a provider, with the customer configuring policy through a web console. They remove the need to deploy and maintain hardware per site and scale with demand which makes them a strong fit for distributed workforces and multi-site organizations.
Why firewalls matter for business security
What is the purpose of a firewall from a business standpoint? It is a control that reduces risk, limits the blast radius when something goes wrong, and produces the evidence auditors and insurers ask for. That is why firewalls remain a baseline investment regardless of company size or industry.
For a business, firewalls deliver several concrete benefits:
- Reduced attack surface by denying inbound traffic to services that should not be exposed.
- Containment of breaches through segmentation, which stops a compromised endpoint from reaching sensitive systems.
- Visibility into who and what is connecting to the network through connection logs.
- Policy enforcement for acceptable use, remote access, and third-party connectivity.
Firewalls also support compliance. For example, PCI DSS requires firewalls between the cardholder data environment and other networks. HIPAA expects access controls and audit logs for systems handling ePHI. GDPR does not name firewalls directly, but Article 32’s requirement for appropriate technical measures to protect personal data makes them a baseline control. Firewall logs are frequently the evidence auditors ask for first.
How to use firewall protection
Firewalls are only as effective as the choices behind them. Choosing the right product, configuring it correctly, and maintaining it over time are the 3 decisions that determine real-world protection.
Choosing the right firewall
The right firewall depends on network size, data sensitivity, and threat profile. A small business with a handful of cloud apps may be well-served by a cloud firewall or a mid-range UTM system. A larger organization handling regulated data usually needs an NGFW with deep packet inspection, intrusion prevention, and application control.
Independent testing matters here. In the CyberRatings.org and NSS Labs 2025 Enterprise Firewall Test the security effectiveness of 7 leading enterprise firewalls ranged from 46.37% to 99.59%—a gap wide enough to make vendor marketing claims a poor substitute for independent lab data. Check published results from CyberRatings, NSS Labs, or similar third parties before you commit.
Configuring the firewall
Once you’ve selected a firewall, the next step is configuring it correctly to maximize its effectiveness. This usually involves setting up rules to control which traffic is allowed in and out of your network. Most firewalls come with default security settings, but it’s important to customize these according to your specific network requirements.
Basic setup steps:
- Define your network zones (e.g., internal, external).
- Set access control rules to permit or block traffic based on IP addresses, ports, and protocols.
- Enable features like logging to monitor traffic and flag potential threats.
- Test the firewall by running simulated attacks to ensure it's blocking malicious traffic.
Maintaining the firewall
Firewalls need regular upkeep to remain effective against developing threats. Maintenance tasks include updating the firewall’s software, applying patches, and reviewing the firewall logs. Keeping an eye on these logs is critical, as they can reveal suspicious activity that requires immediate attention.
Maintenance checklist:
- Regularly update the firewall’s firmware and apply security patches
- Review and fine-tune access rules as your network changes
- Schedule routine log reviews to spot potential threats early on
- Back up your firewall configurations in case of failure or upgrade
Advanced firewall features
Modern firewalls often come with advanced features designed to strengthen security. For example, many include an IPS that detects and blocks malicious activity in real-time. Features like virtual private networks (VPNs) and sandboxing can add additional layers of protection, especially if your business deals with sensitive data or has remote workers. Advanced features to explore:
- Intrusion prevention system (IPS): Automatically monitors and stops network threats
- Deep packet inspection (DPI): Analyzes data in transit for hidden malicious content
- Application control: Lets you manage and monitor the use of specific apps on your network
- Sandboxing Isolates potentially harmful files or code to test them in a secure environment
By choosing the right firewall, configuring it properly, and staying on top of maintenance, you can ensure that your network is well-protected. Don’t forget to explore advanced features for extra security when needed!
Evolution of firewalls
The concept of firewalls originated in the 1980s, borrowing the term from physical firewalls used in building construction to prevent the spread of fire. In networking, early firewalls were simple packet filters embedded in routers.
Their function was basic: to block or allow traffic based on predefined rules for IP addresses, ports, and protocols. These first-generation firewalls were limited in their ability to inspect the content of data packets, which meant they couldn’t detect malicious payloads.
- First generation: Packet filtering firewalls (late 1980s). Inspected individual packets and allowed or blocked them based on predefined rules but could not detect malicious content.
- Second generation: Stateful firewalls (mid-1990s). Tracked active connections and monitored ongoing communication sessions, offering improved detection of suspicious behavior.
- Third generation: Application layer and proxy firewalls (early 2000s). Analyzed traffic at the application layer, providing deeper inspection and more granular control over data exchanges.
- Fourth generation: Next-generation firewalls (NGFW) (2010s). Combined traditional firewalls with advanced features like deep packet inspection, intrusion prevention, and application awareness.
- Fifth generation: Advanced threat prevention (2017 and beyond). Designed to counter large-scale, multi-vector attacks with technologies like anti-bot systems, malware protection, and sandboxing.
Each generation of firewalls has built upon the last, evolving from simple packet filtering to sophisticated systems capable of identifying and stopping modern, complex threats. This trend is still ongoing, and the next shift is already visible in the market.
Firewall vs. antivirus vs. VPN: what is the difference?
These 3 tools are often grouped together, but they solve different problems and work best as a layered set rather than as substitutes for each other.
Tool | What it protects | Where it operates | Primary job |
|---|---|---|---|
Firewall | Networks and the devices behind them | Network boundary or host | Filters traffic by rules; allows or blocks connections |
Antivirus | Individual devices | Endpoint | Detects and removes malicious files and processes already on the device |
VPN | Data in transit | Between endpoint and VPN gateway | Encrypts the connection and masks the user’s IP |
A firewall decides what traffic reaches your network. Antivirus decides what runs on a device once something gets through. A VPN protects the confidentiality of the connection itself, especially on untrusted networks. Running one does not remove the need for the other two.
The future of firewalls
Firewalls are becoming more autonomous, distributed, and tightly coupled with the rest of the security stack. 3 changes stand out.
- First, cloud and as-a-service delivery models continue to displace on-premises appliances for distributed workforces and multi-site organizations.
- Second, machine learning is moving from a bolt-on feature to a core part of traffic classification and anomaly detection.
- Third, Gartner’s 2025 Magic Quadrant for Hybrid Mesh Firewall confirmed what large organizations already knew: a single perimeter no longer exists and firewalls now need to enforce consistent policy across data centers, branch offices, and multiple clouds from one management plane.
Firewalls are also integrating more directly with SIEM SOAR, and XDR platforms, feeding and consuming threat intelligence in real time instead of operating as isolated controls. Their role as a core network security component is not going anywhere.