
Access control is a primary defense mechanism used to protect a company's sensitive data from unauthorized access. In this article, you'll find an overview of access control, covering its fundamental components and practical strategies for implementing such policies.
What is access control?
Access control in cybersecurity refers to the policies, tools, and processes organizations use to regulate who can reach sensitive applications and data. Whether you’re protecting a cardholder data environment or guarding health records, controlling access to network resources is a non-negotiable part of any security strategy.
Access control systems verify user identities through user authentication and assign access rights based on defined roles and responsibilities. They keep unauthorized users out, cutting the risk of data breaches and other cyber-attacks.
This article covers the fundamentals of access management, including:
- Why access control policies matter
- The core components of access control solutions
- Different types of access control systems
- Common access control challenges
Why is access control important?
Effective access control helps organizations serve customers, satisfy regulators, and maintain the systems they depend on. With data breaches making headlines and reputational damage lasting years, strong access control is a business priority, not an optional extra.
At its core, access control prevents unauthorized access and keeps malicious attackers out. But external threats aren’t the only concern. Insider threats, whether from careless employees or compromised accounts, pose just as much risk. Applying the principle of least privilege ensures that users only reach the resources they need for their specific role, limiting the damage any single account can cause.
Without reliable user authentication, attackers can slip past network defenses. Without properly configured authorization settings, they can move freely across systems once inside. This puts confidential data at risk and makes it harder to detect and contain attacks before they spread.
Access control is a major compliance requirement across every industry. HIPAA GDPR PCI-DSS and SOC 2 all require organizations to implement appropriate access control policies that restrict access to sensitive information. The same applies to widely adopted information security standards like ISO 27001.
Access control components
The access control process has 6 main components. Each one plays a specific role in controlling access and protecting network resources.
Identification
This is the first step in any access control model. The user presents a claim of identity, such as a username, email address, or employee ID. However, identification doesn’t verify anything on its own; it simply tells the system who the user claims to be. For example, typing a username into a login screen is an act of identification. What happens next (authentication) determines whether that claim is legitimate.
Authentication
This establishes the user’s actual identity. Every user connecting to the network must prove they are who they claim to be. User authentication could involve a simple password check, but stronger methods like multi-factor authentication provide far better protection. Authentication builds directly on identification: the user states who they are, then proves it.
Authorization
This assigns access rights to network resources. Privileges determine which resources a user can reach and what they can do with those resources. For example, an employee may be authorized to create customer records but not transfer them. Authorization works best when guided by the principle of least privilege, granting only the permissions each role genuinely requires.
Access
The access control system permits entry to network resources so users can carry out their duties according to established access control policies. It ensures the right individuals reach the right tools without exposing unnecessary data.
Well-designed identity and access management processes integrate here to keep permissions consistent across cloud and on-premises environments. By actively monitoring usage patterns, organizations can adjust access quickly when roles change or projects end.
Management
Network administrators must manage user profiles and update access policies as needed. Access control systems allow admins to create and remove users, adjust role assignments, and respond to organizational changes. These systems should integrate smoothly with identity directories for both cloud and on-premises assets.
Auditing
This monitors security levels and identifies weaknesses, such as users holding more access than their role requires, which could create data breach risks. Regular audits confirm that access control policies stay aligned with business and compliance requirements.
Audits also verify that identity and access management processes are working as intended, flagging outdated accounts or unused privileges. Over time, consistent auditing strengthens confidence in your access control system and keeps it resilient against evolving threats.
Access control is a process, not a fixed set of technologies, so, consequently, an effective access control model must be dynamic and flexible.
How does access control work?
Access control can be divided into two broad domains: physical access control and logical (digital) access control. Both are important, but they play very different roles in security systems.
Physical access control
Physical access controls manage access to workplaces and data centers. Controls in this category include:
- Security cards
- Locks
- Biometric scanners
- Cameras to verify individuals.
Logical access control
Logical access control manages access rights to digital infrastructure and confidential data. LAC tends to involve electronic access control methods. This could include passwords and user IDs, as well as MFA.
In practice, organizations usually use both types of access control in their security systems. But in terms of cybersecurity, the critical question is what types of logical controls to put in place.
Some features are common to all access control solutions.
- Access controls use authentication factors to assess user identities This could involve information the user knows (such as a password). It could be something they are (such as a biometric scan). Or the factor could be something the user possesses (such as security tokens or one-time codes).
- Access controls locate the user on the authorization database and assign privileges that fit their identity or role.
- The access system logs information about the user session. This is used to detect anomalies and feeds into regular security audits.
Access systems vary beyond those core features It's important to know the main types when putting in place solid access controls.
Main access control types
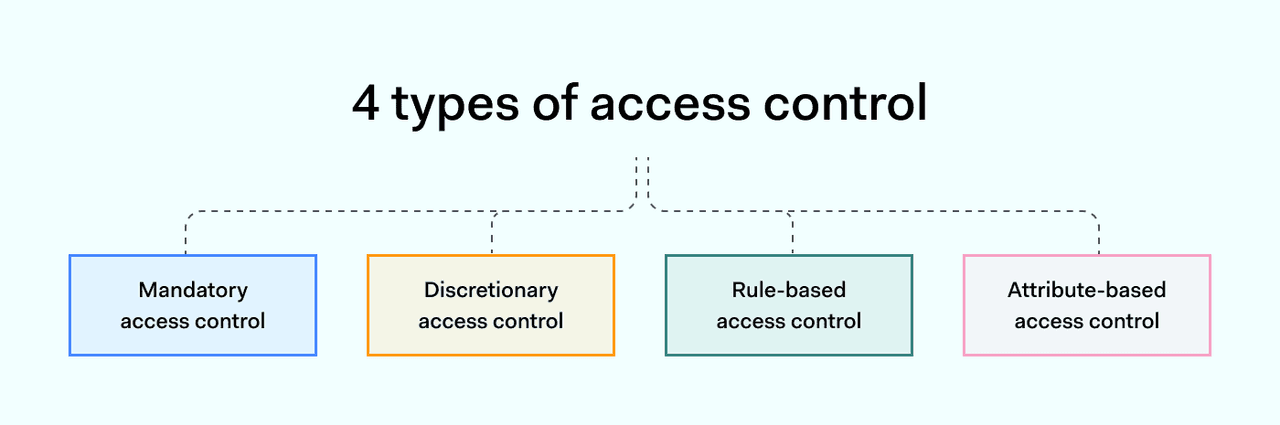
Access control systems come in several forms, each with different strengths and trade-offs. Choosing the right access control model depends on your organization’s size, industry, regulatory requirements, and how sensitive the resources are. Here’s a breakdown of the most common types.
1. Discretionary access control
Discretionary access control (DAC) lets resource owners set access control policies for each asset they manage. Owners can change user privileges, share access, and create role-based groups at their discretion.
DAC works well in fast-moving environments with short-term projects where teams need flexibility. The downside of such discretionary control systems is a lack of centralized oversight. Security teams may struggle to enforce consistent policies when every resource owner makes independent decisions.
2. Mandatory access control
Mandatory access control (MAC) places all access decisions under a single central authority. One governing body defines authentication and authorization policies across all systems, leaving no room for individual resource owners to make exceptions.
MAC can be rigid, but it lets organizations lock down access to their most sensitive resources and restrict entry to pre-approved devices or users. These systems typically rely on clearance levels, granting broad authorizations based on a user’s classification tier. That structure makes mandatory access control a go-to solution in military and government environments.
3. Role-based access control
Role-based access control (RBAC) assigns privileges based on a user’s role within an organization. Each role carries permissions tied to the tasks that position requires. RBAC can span an employee’s full tenure or be time-limited (for example, granting elevated privileges during a specific project).
Like mandatory access control, RBAC is centrally administered. The difference is its focus: RBAC governs how users interact with resources, not just whether they can reach them. A role might carry read access but not write access, for instance.
4. Attribute-based access control
Attribute-based access control (ABAC) uses user attributes, such as location, department, time of day, or device type, as the basis for granting access. After authentication, the system evaluates user, device, environmental, and resource attributes to determine whether access should be granted.
ABAC is an efficient way to manage access to less sensitive resources, and it offers granular control over how those resources are used. It pairs well with other models when organizations need context-aware access decisions.
5. Rule-based access control
Rule-based access control (RuBAC) applies predefined rules to determine whether a user can access a resource. For example, a rule might permit access to certain applications only during business hours or only from devices connected to the corporate network.
Rule-based access control works alongside user authentication, multi-factor authentication, and privilege management. It gives administrators fine-grained controls to govern network access without manually reviewing every request.
6. Policy-based access control
Policy-based access control (PBAC) takes rule-based systems a step further by evaluating access requests against a broad set of organizational policies. Instead of individual rules tied to specific resources, PBAC draws from a centralized policy engine that factors in user role, resource sensitivity, environmental conditions, and compliance requirements, all in a single decision.
PBAC scales well for organizations managing complex environments with many resource types. It reduces policy sprawl by consolidating access logic into one framework rather than scattering rules across individual systems.
7. Break-glass access control
Break-glass access control is an emergency override mechanism. It allows authorized personnel to bypass standard access restrictions when an urgent situation demands it, such as a critical system failure, a medical emergency requiring immediate access to patient records, or an active security incident where responders need elevated privileges on the spot.
Break-glass controls act as a safety valve within an access control model, making sure that rigid security policies don’t create dangerous bottlenecks when speed matters most.
Comparison of the main access control types used in cybersecurity
Type | How access is decided | Best suited for | Key limitation |
|---|---|---|---|
Discretionary (DAC) | Resource owners assign permissions at their discretion | Small teams, fast-changing projects | No centralized oversight and inconsistent enforcement |
Mandatory (MAC) | Central authority sets clearance levels and policies | Military, government, high-security environments | Rigid and slow to adapt to change |
Role-based (RBAC) | Permissions tied to organizational roles | Mid-to-large enterprises with defined job functions | Role explosion in complex organizations and roles can become too broad |
Attribute-based (ABAC) | User and environmental attributes evaluated in real time | Context-sensitive access, large or diverse user bases | Complex to configure and maintain |
Rule-based (RuBAC) | Predefined rules (time, location, device) govern access | Supplementing other models with conditional logic | Rules can multiply and become hard to manage |
Policy-based (PBAC) | Centralized policy engine evaluates multiple factors per request | Complex, multi-system environments needing unified governance | Requires significant upfront policy design |
Break-glass | Emergency override of normal restrictions | Crisis situations (system outages, medical emergencies, incidents) | Risk of misuse if logging and review aren’t enforced |
Benefits of access control
Access controls are an essential cybersecurity tool for several reasons:
Reduced risk of data breaches
Authentication admits legitimate users and blocks those without credentials. Privileges limit the power of attackers if they steal credentials. This presents a major obstacle for data thieves.
Compliance with data protection regulations
Poor data security can lead to massive financial or even criminal penalties. Robust access controls limit access to confidential data, in line with HIPAA or PCI-DSS regulations
Enhanced network visibility
Companies manage large communities of devices and users. Solid access controls help to manage connected devices. Only users with the right credentials can connect to sensitive resources. Devices and users must be logged and identified before they are granted access.
Access control challenges
Managing access is never simple, even in smaller organizations. The task becomes even more difficult with hundreds of users, sprawling SaaS subscriptions, and a mix of on-premises, cloud, and hybrid resources. Here are the most common challenges security teams face.
- Creating centralized user directories. All users should be visible to security managers through a single, unified directory. But when resource owners manage access control policies independently, unsecured application silos can emerge. Without centralized oversight, access control systems lose consistency, and gaps appear that attackers can exploit.
- Unsafe user behavior. Users may rely on weak passwords, connect through insecure public Wi-Fi, or add unmanaged devices to the network. Strong user authentication practices, including multi-factor authentication and device verification, help catch these risks. But technology alone isn’t enough. Regular training should make sure all staff follow cybersecurity best practices.
- Managing multi-cloud and hybrid environments. Many organizations now operate across multiple cloud providers, on-premises infrastructure, and dozens of SaaS applications. Each platform comes with its own access control model, permissions structure, and admin console. Keeping policies consistent across AWS, Azure, Google Cloud, and a growing stack of SaaS tools creates a significant coordination burden. Without a unified approach, access gaps and misconfigurations multiply fast.
- Shadow IT. When employees adopt unauthorized apps, cloud services, or tools without IT approval, they create blind spots that sit entirely outside the organization’s access control systems. Security teams can’t enforce policies on resources they don’t know exist. Shadow IT is especially common in organizations where provisioning new tools through official channels is slow or cumbersome, which pushes users to find their own workarounds.
- Over-privileged accounts. Users frequently accumulate permissions over time as they move between teams, take on temporary projects, or receive one-off access that never gets revoked. This violates the principle of least privilege and widens the blast radius if an account is compromised. Regular audits and automated access reviews are the most effective way to catch and correct over-privileged accounts before they become a liability.
- Reporting and audit readiness. Access control systems must log every access request and generate reports that satisfy auditing and regulatory compliance requirements. In larger organizations, the volume of access data makes this a real operational challenge, particularly when logs are scattered across multiple platforms, and there’s no centralized reporting layer.
How to implement access control
Putting access control into practice requires a structured approach that ties security policies to how your organization actually operates. Here’s a step-by-step framework to get it right:
- Map your assets and data flows. Identify every system, application, and data store that needs protection. Catalog who currently accesses each resource and how. You can’t build an effective access control model without a clear picture of what you’re protecting.
- Define access control policies. Establish written rules that specify who can access what, under which conditions, and with what level of permission. Ground these policies in the principle of least privilege: every user should receive only the access their role genuinely requires, nothing more.
- Choose the right access control model. Evaluate whether role-based access control, attribute-based access control, or a hybrid approach fits your environment. The decision depends on your organization’s size, regulatory requirements, and the dynamism of your workforce. Most mid-to-large organizations benefit from combining models.
- Deploy identity and access management tools. Implement access control systems that automate user provisioning, enforce authentication policies, and centralize permission management. These tools should support both cloud and on-premises environments, and integrate cleanly with your existing identity directories.
- Enforce strong user authentication. Require multi-factor authentication across all critical systems. Passwords alone are no longer sufficient. Layer in device verification, adaptive authentication, or biometric checks where the risk level warrants it.
- Educate your employees. Train teams on why access policies exist and what’s expected of them. Cover password hygiene, device security, and how to report suspicious access. Even the best access control systems can be undermined by uninformed users.
- Audit and review regularly. Schedule periodic access reviews to catch privilege creep, remove inactive accounts, and verify that permissions still match each user’s current role. Automated access reviews help keep this manageable at scale.
- Plan for exceptions. Build a documented process for emergency access scenarios, including break-glass procedures with full logging and post-incident review. Rigid systems that can’t accommodate real-world urgency create their own risks.
These steps give you a strong starting point, but the way organizations think about access control is shifting. Traditional, perimeter-based security architectures often rely on network location as a trust signal. Zero-trust network access (ZTNA) removes that assumption entirely. Under a zero-trust approach, every access request is verified individually, regardless of where the user is connecting from or whether they’ve already authenticated in a previous session. Identity, device health, location, and behavior all factor into every decision.
For organizations operating across multi-cloud, hybrid, and remote work environments, zero trust has become the practical foundation for modern access control implementation. It ties together user authentication, the principle of least privilege, and continuous monitoring into a single framework that adapts in real time, rather than relying on static perimeter defenses.
Access control best practices
A well-chosen access control model only delivers results if it’s backed by consistent, practical habits. These best practices help organizations keep their access control systems effective as teams grow, tools change, and threats evolve.
- Enforce multi-factor authentication. Require MFA across all critical systems and sensitive data. Passwords get stolen, guessed, and reused. Adding a second layer of user authentication, whether it’s a one-time code, biometric check, or hardware token, reduces the chance of unauthorized access.
- Apply the principle of least privilege. Give every user, service account, and application only the permissions they need to do their job, nothing more. Start with minimal access and add privileges only when there’s a documented reason. This limits the scope of damage if any single account is compromised.
- Conduct regular access reviews and deprovision promptly. Schedule quarterly (or more frequent) reviews to catch privilege creep, orphaned accounts, and outdated role assignments. When employees leave or change roles, revoke their previous access immediately. Delayed deprovisioning is one of the most common access control gaps attackers exploit.
- Segment your network. Break your network into isolated zones so that access to one segment doesn’t grant a path to everything. Network segmentation contains breaches, slows lateral movement, and gives security teams more time to detect and respond to threats before they spread.
- Monitor and analyze access logs. Collect access logs from every system and review them for anomalies: logins from unusual locations, access attempts outside business hours, sudden spikes in privilege usage. Without automated alerting, this doesn’t scale, and logs that nobody reviews are just storage costs.
Wrapping up
Access control in cybersecurity is the backbone of how organizations protect their data, systems, and people. From choosing the right access control model to enforcing the principle of least privilege and adopting zero trust, every layer matters. The specifics will look different for every organization, but the goal stays the same: make sure the right people reach the right resources, and no one else does.