Control how your traffic is routed with VPN split tunneling for business
Choose which destinations use the VPN tunnel and which bypass it to balance security, performance, and network efficiency.

14-day money-back guarantee
OFFICIALLY ENDORSED
Chosen by industry experts and thought leaders
Join 15,000+ business teams worldwide who trust NordLayer for fast, reliable network protection, with split tunneling VPN built into every plan.
OVERVIEW
What is VPN split tunneling?
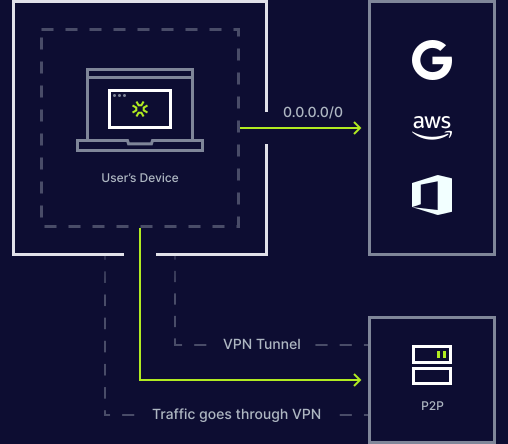
VPN split tunneling gives you control over how your network traffic is routed by allowing you to choose which traffic goes through an encrypted VPN tunnel and which connects directly to the internet. Instead of sending all traffic through the VPN, split tunneling lets organizations define which destinations require VPN protection and which can benefit from a direct connection.
FUNCTIONALITY
How does VPN split tunneling work?
Split tunneling applies routing rules that decide which traffic uses the VPN tunnel and which traffic bypasses it, and NordLayer gives you 3 ways to set those rules.

Include mode
Route selected IP addresses and subnets through the VPN tunnel, while all other traffic connects directly to the internet, so access to private resources stays protected without pulling everyday browsing through your gateway.

Exclude mode
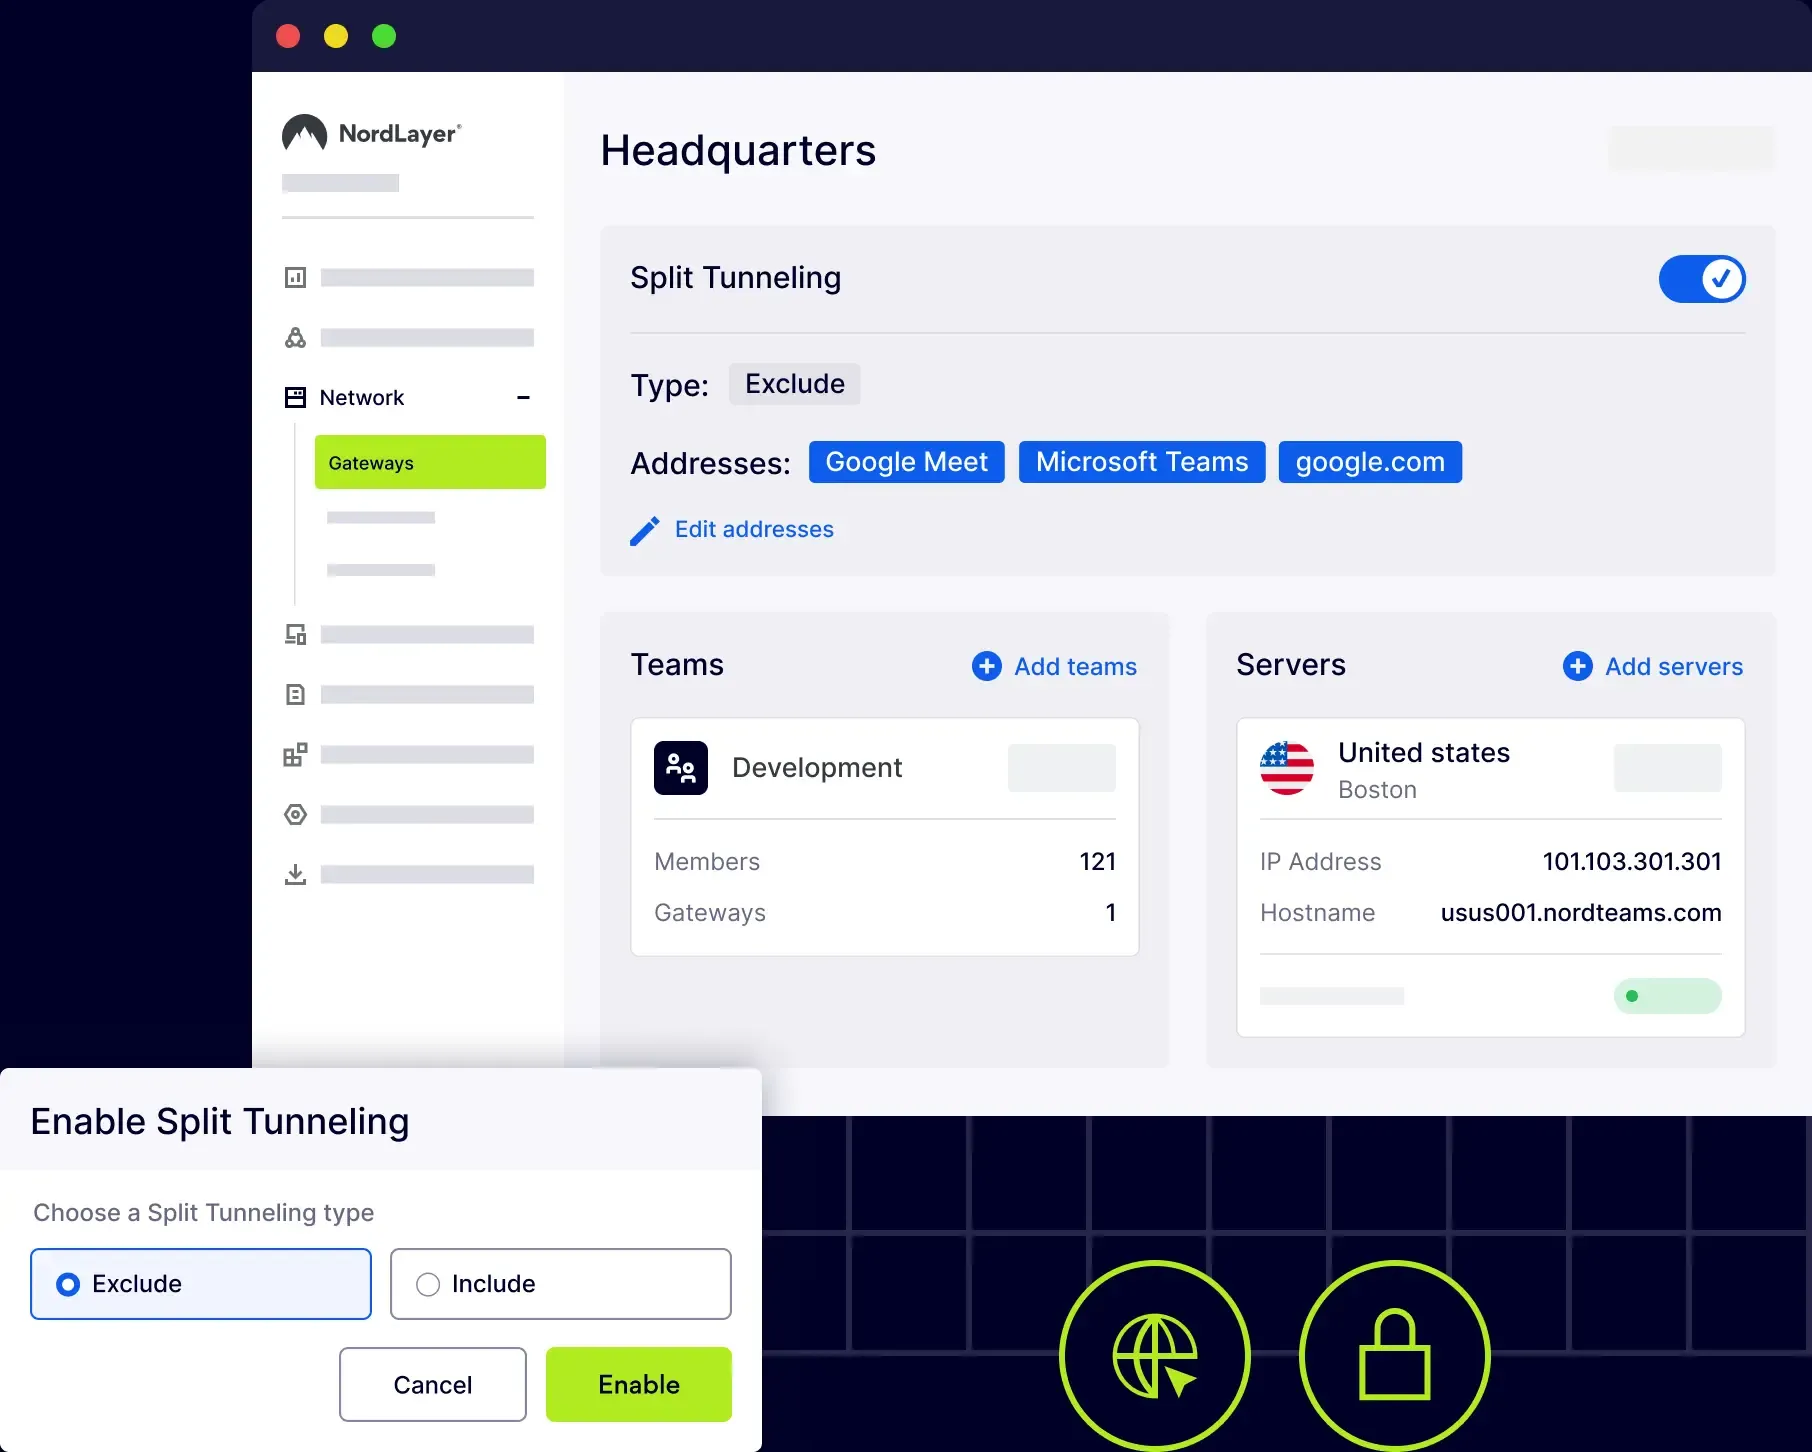
Route everything through the VPN tunnel by default, and name the exceptions, so protection stays broad while services like video conferencing platforms or VPN-restricted sites connect directly for better performance.

URL-based split tunneling
Set domain-level exceptions through the NordLayer browser extension for Chrome, Firefox, Brave, and Edge, so a named site bypasses the tunnel while the rest of your browsing stays protected, with no client reconfiguration needed.
benefits
Why use split tunneling?
Full tunneling sends every packet through your gateway, costing you speed, bandwidth, and infrastructure headroom. Split tunneling lets you decide where protection is worth the overhead and where a direct connection would be a better fit.

Improve your network performance
Route latency-sensitive traffic like video calls straight to the internet, so your team stops blaming the VPN for a frozen meeting.

Maintain security where it matters
Critical traffic stays inside the encrypted tunnel under admin-defined policy, so nothing bypasses the VPN unless you decide it should.

Reduce infrastructure load and cost
Take unnecessary traffic off your gateways and corporate network, freeing bandwidth and delaying the next capacity upgrade.

Set the rules once, apply them everywhere
Define the routing policy per team from the Control Panel and roll it out across every device without touching a single endpoint.
COMPARISON
Split tunneling vs. full tunneling: which routing model fits your network?
Full tunnel VPN
A full tunnel VPN routes everything through your gateway by default, which gives you complete visibility over every session at the cost of speed and capacity.
Every connection leaves the device through the encrypted tunnel, regardless of destination.
Latency-sensitive traffic like video calls competes with everything else for gateway capacity.
Gateway capacity has to scale with total traffic, including traffic that gains nothing from encryption.
One unified routing policy covers everyone, with little flexibility to tune it per user or team.
Environments where every session has to be inspected or logged centrally.
Split tunneling
Split tunneling lets you decide which destinations need the tunnel, so protection stays on your private resources while everything else takes the direct route.
You define which destinations use the tunnel and which connect directly.
Traffic that does not require inspection takes the fastest route available.
Only the traffic you nominate reaches the gateway, so capacity goes further.
Include, exclude, and URL-based rules are set per team from the Control Panel.
Teams balancing protection with day-to-day performance across mixed workloads.
Start split tunneling your traffic from just $11 per user/month

Split tunneling is available on the NordLayer Core plan from just $11 per user/month. Upgrade to NordLayer Premium from just $14 per user/month to add URL-based split tunneling. Both plans require a 5 user minimum and offer a 14-day money-back guarantee.
USE CASES
3 big problems split tunneling helps solve
Improve video conferencing performance
Allow collaboration platforms to bypass the VPN tunnel while keeping other traffic protected.

Access VPN-restricted services
Create exceptions for websites or services that do not work properly through VPN connections.

Optimize remote work connectivity
Balance secure access to company resources with fast access to public internet services.
GETTING STARTED
How to set up VPN split tunneling
Follow these 3 simple steps to enable NordLayer VPN split tunneling across your network.
- 1
Sign up for NordLayer
Choose our Core or Premium subscription plan and download the NordLayer app.
- 2
Enable split tunneling
Pick include, exclude, or URL-based mode and define which destinations will use the tunnel.
- 3
Roll it out to your teams
Apply the policy in the Control Panel and your team gets faster connections without losing protection.
NordLayer + CrowdStrike: secure your network and endpoints all at once
With threats coming from all sides, your business can’t afford to leave anything unprotected. NordLayer and CrowdStrike secure both your company network and employee devices, so your teams stay safe and productive.
Monitor and control who can access your company network.
Stop threats like malware and phishing with AI-powered protection.
Keep your business compliant with the latest data security standards.


Get a real-time look at how NordLayer protects businesses
Explore features like Custom DNS, a dedicated IP, VPN Split Tunneling, and more, all in real-time with our interactive Control Panel demo.

DIVE DEEPER
Expand your knowledge


CYBERSECURITY LEARNING CENTER
Advantages of using a VPN
MORE INFORMATION
Frequently asked questions
There are 3 common types. Application-based split tunneling routes traffic based on which app is making the request. IP or subnet-based split tunneling routes traffic based on the destination address, which is what NordLayer’s include and exclude modes use. URL- or domain-based split tunneling applies rules to specific websites, which NordLayer supports through the browser extension.
Yes, NordLayer allows you to control which traffic goes through the VPN tunnel and which traffic bypasses it. With split tunneling, you can use include mode to route selected IP addresses or subnets through the VPN tunnel while other traffic connects directly to the internet. Alternatively, you can use exclude mode to allow specific IP addresses, subnets, or domains to bypass the tunnel. The browser extension also supports URL-based split tunneling for managing domain-based exceptions.
Split tunneling and full tunneling differ in how traffic is routed. Full tunneling sends all network traffic through the VPN tunnel, providing centralized security and control. Split tunneling allows organizations to choose which traffic uses the VPN tunnel and which traffic bypasses it, helping balance security, performance, and access requirements. NordLayer supports flexible split tunneling options with include, exclude, and URL-based modes to adapt routing based on organizational needs.
The risk with split tunneling is that traffic leaving the tunnel is no longer inspected or encrypted by the VPN, so a poorly scoped rule can send sensitive traffic over an untrusted network. NordLayer removes most of that exposure by keeping the decision with the administrator rather than the end user. Exclude mode protects everything by default and only releases the destinations you name, so the safe path is the one you get unless you actively change it. Every rule is set and audited from the Control Panel.
Split tunneling is as safe as the policy behind it. Traffic that bypasses the tunnel takes the same path as any ordinary internet connection, so if a device is working from a compromised network, that traffic is exposed in the same way normal browsing would be. What keeps that from reaching the rest of your network is scoping the exceptions tightly, keeping private resources inside the tunnel, and applying the rules centrally instead of letting users configure their own. With NordLayer, administrators define every exception from the Control Panel and can pair split tunneling with a Kill Switch, so protected traffic never falls back to an unsecured connection.
To disable split tunneling, administrators can turn off the feature in the relevant gateway or browser extension settings. After disabling split tunneling, traffic will no longer follow custom routing rules and will instead use the default VPN routing behavior.
No, not all VPNs offer split tunneling. Split tunneling requires advanced traffic routing capabilities that allow users or administrators to define which traffic goes through the VPN tunnel and which traffic bypasses it. NordLayer provides flexible split tunneling options with include and exclude modes, helping organizations balance security, performance, and network efficiency.
No, split tunneling and a VPN kill switch are different NordLayer security features. Split tunneling gives administrators control over traffic routing by defining which destinations use the VPN tunnel and which bypass it. A VPN Kill Switch prevents data exposure by blocking internet access if the VPN connection is interrupted. Together, these features help organizations balance security, reliability, and performance.