Summary: Access control lists filter network traffic and decide who can access which resources. Learn how ACLs work, where to place them, and why they matter.
Does your business rely on access control lists (ACLs) to manage user access? If not, you're not alone. Many organizations shy away from them due to the challenges of maintaining numerous lists across different network areas. However, an access control list provides an extra layer of security for your network in specific scenarios and can be paired with role-based access control (RBAC).
This article explores how access control lists can streamline access management and help protect sensitive information. Read on if you want to understand how ACLs fit into your network's security strategy.
An access control list defined
An access control list (ACL), sometimes called an access list, filters network traffic based on source and destination. It's a set of rules that determines which users can access particular network resources and data. Users who are not included on the ACL are denied access to them.
ACLs also complement role-based access control (RBAC). For example, an ACL can be configured to allow only members of a development team to access a specific codebase while blocking other users with DevOps roles who aren't involved in the project.
An access control list (ACL) is a vital tool for managing permissions in systems and networks. Here’s what they do:
Control user access and protect data. ACLs decide who gets in, what they can access, and help keep intruders out.
Help meet compliance requirements. Many cybersecurity standards and certifications require network access control and network restrictions. ACLs can be one way to meet those requirements.
Regulate dataflow. Network ACLs control traffic based on criteria like IP addresses, protocols, and ports. In contrast, resource ACLs govern specific file or system permissions. For example, a network administrator may be granted read, write, and edit permissions for sensitive files, while a guest user may only have view-only access. This approach ensures that both the transmission path and the data itself are selectively secured.
Work across your whole infrastructure. You can deploy ACLs on routers, switches, VPNs, and databases, which gives you one clear way to manage access network-wide.
Improve performance and security at once. By blocking unwanted traffic and giving IT admins granular control, ACLs keep systems safe and running smoothly.
How ACLs work
ACLs play a critical role in traffic control by guiding the flow of data throughout the network.
Each ACL contains rules that define who or what can access a resource. For files and systems, these rules (ACEs) typically list user or group names and their specific permissions. In contrast, network ACLs use technical criteria like IP addresses, ports, and protocols to filter traffic. Whether managing files or data flow, ACLs provide a structured, rule-based approach that helps administrators maintain control over their resources.
Rule creation and ordering
ACLs use predefined rules to allow or deny packets, and the order of these rules is critical to your business protection. Each list is made up of smaller pieces called access control entries (ACEs). These entries state a specific condition and an action—usually permit or deny.
The process starts with rule creation and ordering, where admins set up ACL rules in a precise sequence. Because the system checks these rules from the top down, the order determines which rule is matched first. Once a packet matches a rule, that permit/deny action is applied. Setting up rules in a specific sequence ensures your most critical security policies are enforced before general traffic rules can apply.
Packet evaluation
This is another key function of ACLs, where the data within each packet is checked against the ACL rules to decide if it should be allowed through or blocked. This evaluation is based on criteria like IP addresses, port numbers, and packet content, matching your security measures.
Default actions
For file systems, ACLs detail specific user access privileges to system objects such as files and directories, dictating actions like reading, writing, or executing based on the user’s role (e.g., administrator or guest).
This granularity extends to default actions, where ACLs apply predetermined responses when a packet or access request does not meet any of the specified rules. Typically, this results in denial of access to protect network integrity.
The placement of ACLs depends on the type of the list.
Standard ACLs (the “destination” rule). Add these closest to the destination network. Because they only check the source IP address, placing them near the source can accidentally block legitimate traffic from reaching valid parts of your network.
Extended ACLs (the “source” rule). Place these closest to the source of the traffic. These lists are more detailed—they check ports and protocols—so adding them near the source prevents bad traffic immediately.
You can also choose the location of the ACL based on its functional purpose:
The network edge (DMZ). ACLs can filter traffic before it reaches your system. In practice, this means putting a routing device with an ACL between your demilitarized zone (DMZ) and the internet. This is important because your web servers, DNS, and other publicly exposed assets are in the DMZ.
Internal network. You can also place ACLs between the DMZ and the rest of your internal network. The two placements—one between the DMZ and the internal network and the other between the DMZ and the internet—need different configurations, each tailored to protect a specific system that is behind it.
Cloud environments. In cloud-based systems, you can apply network access control lists (NACLs)at the subnet level to provide a virtual firewall for specific cloud segments.
The edge ACL shields your DMZ from the open internet, while the internal one protects your users and systems from anything that makes it into the DMZ. Using both works best. If one ACL misses something, the other is there to catch it.
Types of access control lists
It’s worth remembering that you can only set these up as named extended ACLs. There are various types of access control lists, which serve different purposes based on their functionality and scope.
Filesystem ACLs
These ACLs help control access to files and directories inside an operating system.
Linux ACLs enable admins to enforce granular permissions that extend beyond basic categories, such as user or group.
Windows ACLs, with their user-friendly interface, make defining file permissions easier.
Networking ACLs
These regulate network access by providing instructions to network switches and routers. Networking ACLs specify the types of traffic allowed to interface with the network and define user permissions within the network.
They are categorized according to their traffic filtering capabilities:
Standard ACLs are limited in scope and concentrate only on the source IP addresses.
Extended ACLs offer more granular control and flexibility. They filter traffic based on source and destination IP addresses, protocols, and port numbers.
Like firewalls, networking ACLs control network traffic.
Numbered vs. named ACLs
We categorize these based on how an ACL is identified and managed on a device.
Numbered ACLs
They are identified by a number from a specific range:
1–99 and 1,300–1,999 for standard ACLs
100–199 and 2,000–2,699 for extended ACLs
There are 2 downsides to numbered ACLs:
The numbers don’t tell you anything about what the list actually does, and editing them is a pain.
Need to remove or insert a single rule in the middle? Traditionally, you’d have to delete the entire list and retype it (unless you’re using sequence-based editing).
Named ACLs
These replace the number with a custom alphanumeric string or name, such as “block_web_traffic,” which makes reading large configurations much easier. Named ACLs let you insert, update, or delete individual rules with sequence numbers, without deleting the list.
Dynamic (lock-and-key) ACLs
Dynamic ACLs—often called lock-and-key—give temporary access to a user or host only after they authenticate through Telnet or an authentication server. They work in 3 steps:
Create an extended ACL rule that blocks the incoming traffic you want to control.
When the user is authenticated, the router or firewall temporarily adds a dynamic permission to the active ACL.
After the session times out or the user disconnects, the temporary permission is automatically removed.
Reflexive ACLs
They enhance standard filtering by bringing session awareness to it and letting legitimate response traffic back in by generating temporary entries on the fly. Here’s how it works:
A reflexive ACL monitors traffic leaving your internal network.
When a device inside the network initiates a connection, the router logs the session parameters and briefly opens the ACL for the corresponding replies.
As soon as that session closes, the opening closes with it—any unsolicited traffic from outside still gets dropped.
The benefits of using an access control list
Better network performance. Filtering out unnecessary traffic frees up bandwidth for what actually matters.
Stronger security. Admins can configure access lists to match their exact needs, keeping unwanted packets from entering the network.
Granular traffic control. You decide what gets permitted or denied, based on your network’s specific requirements.
ACL vs. RBAC: what’s the difference?
Both role-based access control (RBAC) and ACLs are about access control, but they approach it in very different ways.
RBAC ties permissions to roles rather than to individuals. First, you define a role, such as "HR Manager" or "Network Admin.” Then, you attach permissions to the role and assign users to it. Need to change what everyone in a role can do? Update the role once, and the change applies to everyone. That’s why RBAC scales well in larger organizations.
ACLs, on the other hand, attach permissions directly to objects, such as files or resources. Each object carries its own list of who can do what with it. That gives you fine-grained control over individual resources, but it gets messy fast when you’re managing hundreds of users and objects.
Here is how they differ:
RBAC
ACLs
How it works
Assigns permissions through roles.
Define which users or groups can access specific resources.
Permissions
An access list with permissions is attached to a resource.
Access is defined based on a job role.
Managing changes
You manage users and their roles.
You manage access to the resource.
Granularity
High. Many users can be managed at the same time.
High. When users and files grow, it becomes more challenging to manage them.
Typical use
Large organizations or growing businesses where roles define what data employees can see.
Fine-grained permissions for specific resources.
Drawbacks
Lacks flexibility
If, for example, one user needs a permission exception that doesn’t come with their role.
Hard to scale in large organizations
Managing permissions user by user causes an IT burden.
In practice, many organizations use both RBAC for broad access policies and ACLs for granular, resource-level control.
Enhancing device security with ACLs
While ACLs offer significant advantages in network security, it's essential to extend this protection to device-level security. By adopting device posture security (DPS), your organization can evaluate the security of devices connecting to the network.
Through DPS, you can evaluate and monitor devices according to your predefined rules. But that’s not all. You can also automatically restrict network access for accounts using non-compliant devices. This integrated approach enhances overall network security by addressing vulnerabilities at both the network and device levels.
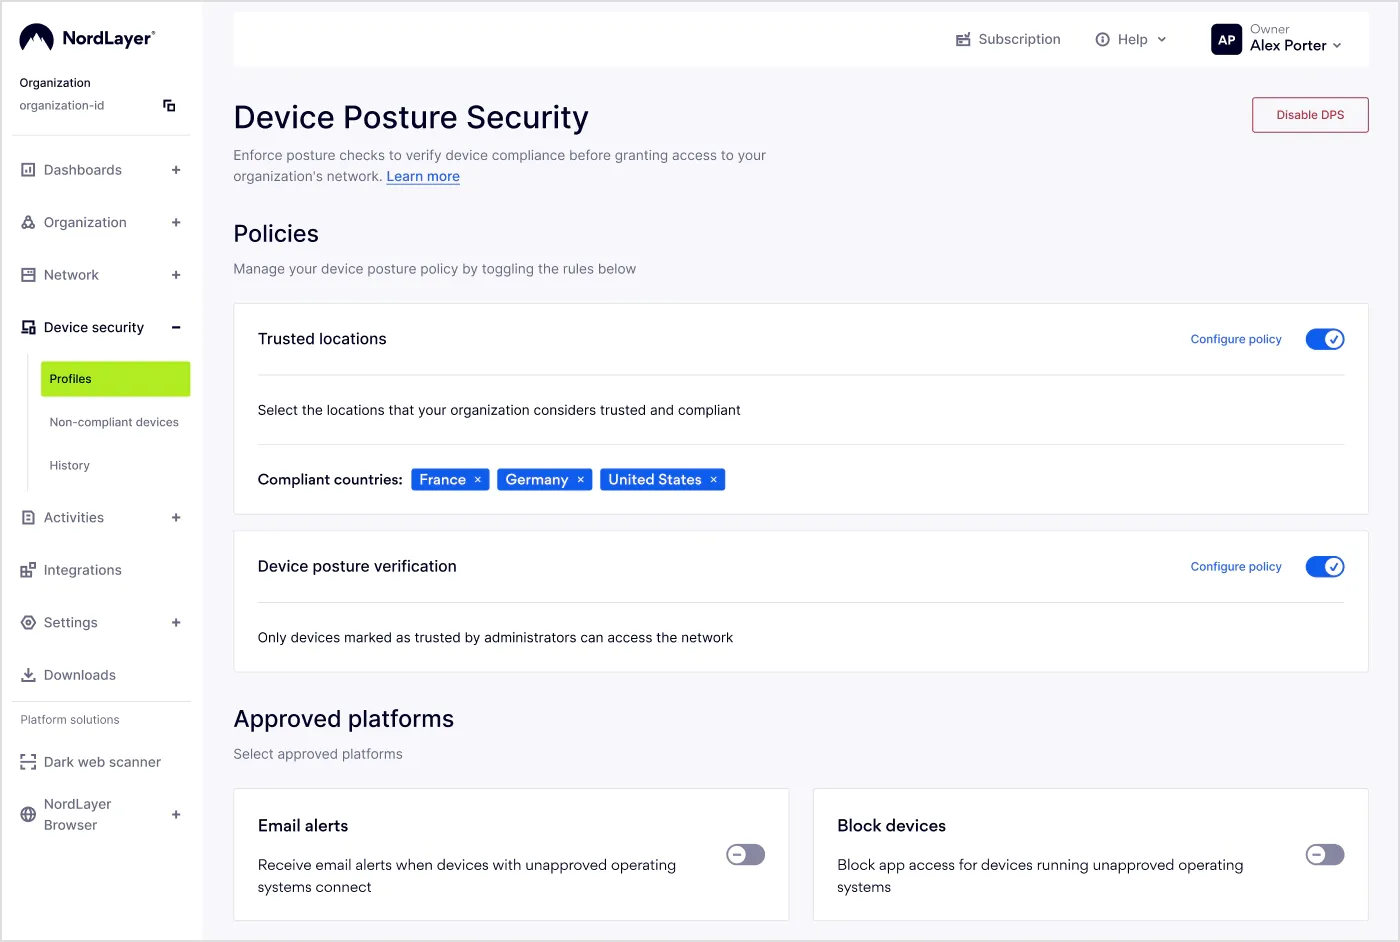
IT administrators can easily implement ACLs for device posture security (DPS) using our web-based Control Panel. To enable DPS checks, create various rules such as existing file check, OS version, jailbreaking or rooting status, and device location.
Setting up ACLs in the panel is simple. Just create a profile and specify the desired rules. Once configured, it’s important to test the ACL to ensure that it is functioning as expected. Finally, activate the ACL to start enforcing the specified access control rules on your network.
Creating a profile in the device posture security feature in NordLayer's Control Panel
ACLs for internal network segmentation
Protecting your data from leaks and insider threats is more crucial now than ever. It's not just about safeguarding information; it’s about maintaining the credibility of your business. That’s where access control lists (ACLs) come in. They act as gatekeepers, deciding who gets access to what within your network. By setting up ACLs, you can stop unauthorized users from moving laterally through your network, helping to prevent data breaches.
Additionally, when you combine ACLs with role-based access control (RBAC), you gain even more control over who can access different parts of your network. With our cloud firewall, you can optimize your network by implementing granular segmentation using ACLs. These lists act as virtual bouncers, controlling who can access which parts of your network.
Our intuitive Control Panel facilitates the creation and management of ACLs, providing a streamlined and centralized approach to network security management.
ACLs in external access control
Managing network access isn't just about your team. You also have to consider third-party vendors, contractors, and other external partners who might need access to your systems.
With access control lists, you can ensure that these third parties only have access to the specific resources they need, minimizing the risk of unauthorized access and potential security breaches.
By setting up granular segmentation and ACL rules, you can protect your network against potential threats while enabling collaboration with external partners. Our cloud firewall feature makes managing external access easy, ensuring your network is protected from all angles.
ACL best practices
ACLs are only as effective as the rules behind them. Follow these industry standards to keep your network secure and its performance high:
Use role-based (group) rules. Assign permissions to security groups or roles, not individual users.
Order your rules strategically. Place your most frequently matched (hot-path) rules at the top of the list. Also, always add specific deny rules above broad permit rules to prevent security overlap.
Position your ACLs correctly. Follow the “source-destination” rule of thumb: place extended ACLs close to the source to save bandwidth, and standard ACLs close to the destination to avoid blocking legitimate traffic.
Audit and document your ACLs on a regular basis. Check your rules periodically to remove “orphaned” entries—rules for employees who have left or systems that no longer exist. Logging changes is essential for maintaining a clear audit trail for compliance.
Take control with NordLayer’s advanced network access
Access control lists (ACLs) make role-based access control more precise. They help ensure only the right people have access to your data and resources, and they improve network performance. They’re a frontline defense against unauthorized access and potential breaches.
The benefits of ACLs don't stop there. By combining ACLs with our cloud firewall, you add an extra layer of security to your network. With NordLayer, setting up and managing ACLs is simple.
Ready to take your network access control to the next level? Contact us today to learn more about how you can combine RBAC and ACLs to protect your resources.
Joanna Krysińska
Senior Cybersecurity Copywriter
Joanna writes about zero trust, network security, access control, and threat prevention, but her cup of tea is compliance and how regulations shape security controls.
Her work also includes the dark web topics and the methods cybercriminals use to target companies, such as social engineering or ransomware attacks, for example.