Summary: Attack surface management (ASM) monitors and mitigates security risks across an organization’s cloud and IT assets to reduce potential entry points for attackers.
Attack surface management (ASM) is a proactive cybersecurity approach that maps and mitigates security risks from an attacker’s perspective (taking an outside-in view of everything a company exposes across its cloud and IT assets). ASM inspects your organization the way a cybercriminal would, then works to reduce the entry points they could reach. Its goal is attack surface reduction and cutting the paths attackers could use to breach your network perimeter.
ASM secures everything your company uses (both inside your office and online) that a cybercriminal could discover and exploit. This way, businesses can defend against data breaches, malware infections, and other threats targeting their cloud infrastructure and sensitive data stores.
Key takeaways
Attack surface management (ASM) identifies, classifies, prioritizes, and monitors all potential entry points for cyberattacks on an organization's digital assets.
Core attack surface management functions are asset identification, risk classification, prioritization of vulnerabilities, and continuous monitoring.
Attack surface management implementation involves vulnerability analysis, evaluating providers, and establishing policies after deployment.
Vulnerability management identifies, analyzes, and resolves security risks across networks and devices.
Organizations can mitigate attack surface risks through zero-trust policies, secure remote access, strong authentication, and protective backups.
What is an attack surface?
An organization's attack surface refers to the total sum of vulnerabilities, weaknesses, and potential entry points that threat actors could exploit to gain unauthorized access to systems or data. The larger the cyberattack surface, the more exposed assets there are, the higher the risk of a successful breach.
Attack surface management focuses on identifying and reducing these exposure points.
Key components of an attack surface
The entire attack surface is made up of several core components:
Known assets
These are the IT assets, like devices, applications, and infrastructure, that an organization's security teams are aware of and have intentionally provisioned on the network. Known assets undergo regular monitoring and security posture assessments.
Unknown assets
Unknown assets are assets that the security team has not inventoried or is unaware of. They can include shadow IT, orphaned systems, forgotten cloud resources, and unmanaged devices.
Rogue assets
Rogue assets are unauthorized or malicious assets that can expose or target an organization. Examples include unauthorized devices, phishing websites, typosquatted domains, and fake applications impersonating the company.
Vendor connections
Beyond just internal assets, an organization's vendors and third-party integrations expand the external attack surface. Cloud providers, SaaS tools, contractors, and partners may introduce new vulnerabilities to monitor and secure.
Organizations can methodically reduce their overall cyber risk exposure over time by continuous asset discovery and evaluating all these components that make up the externally exposed digital attack surface.
Different types of attack surfaces
An organization's attack surface isn't just its networks and software. It also includes physical assets and the people within the company. Understanding the different types of attack surfaces is crucial, as each presents its own risks and requires its own strategies for assessment and mitigation.
Physical attack surface
An enterprise’s physical attack surface includes all of its hardware, such as computers, mobile devices, external storage drives, laptops, and IoT machinery. This surface can be exploited through various means, including insider attacks, stolen equipment, improper disposal of old hardware, and negligence by remote teams.
Digital attack surface
Due to the widespread adoption of cloud computing technologies, the digital attack surface presents more complex risks. It includes misconfigurations, poor identity access management (IAM), publicly exposed resources, and unofficially commissioned resources, also known as shadow IT.
Social engineering attack surface
The social engineering attack surface refers to an organization's human element, including individuals' vulnerability to manipulation and deception. Unlike technical exploits, social engineering attacks target human emotions, cognitive biases, and a lack of awareness to trick users into compromising security.
Cloud and API attack surface
Cloud services and the application programming interfaces (APIs) that connect them form one of the fastest-growing parts of a modern attack surface. Common vulnerabilities include misconfigured access permissions, publicly reachable databases, over-privileged accounts, and unauthenticated or poorly authenticated APIs. Every storage bucket, container, serverless function, and API endpoint is a point that has to be found and secured.
APIs deserve separate attention because they now carry most application traffic and are a top target. Shadow APIs (endpoints running without the security team’s knowledge) and zombie APIs (deprecated versions left online) widen the surface further, because neither is monitored or patched. Reducing this surface means keeping an inventory of every cloud resource and API, enforcing least-privilege access, and removing endpoints no longer in use.
AI attack surface
AI systems add exposure points that older security tools were not built to check. LLMs, the data used to train them, and the agents and integrations built on top of them each introduce risks. Common attack methods include prompt injection, where crafted input overrides a model’s instructions to make it leak data or perform unintended actions; training-data poisoning, where an attacker corrupts the data a model learns from; and model output that exposes sensitive information the system had access to.
AI agents that call tools, query databases, and act on their own expand the surface again, because each connection and permission an agent holds becomes something an attacker can try to abuse.
Reduce breach risk across endpoints and access
Combine secure access with advanced endpoint detection and response to identify, contain, and manage threats across your environment.
Attack surface management is crucial because it helps organizations gain visibility and control over an increasingly complex IT ecosystem with many potential entry points for attackers. The organization's attack surface expands rapidly as businesses adopt cloud services and remote work solutions and integrate with more third parties.
Unpatched vulnerabilities in any of these exposed areas can lead to crippling data breaches. Comprehensive attack surface monitoring and mitigation allow teams to stay ahead of emerging threats by continuously identifying and resolving security weaknesses and gaps before they are exploited.
How does attack surface management work?
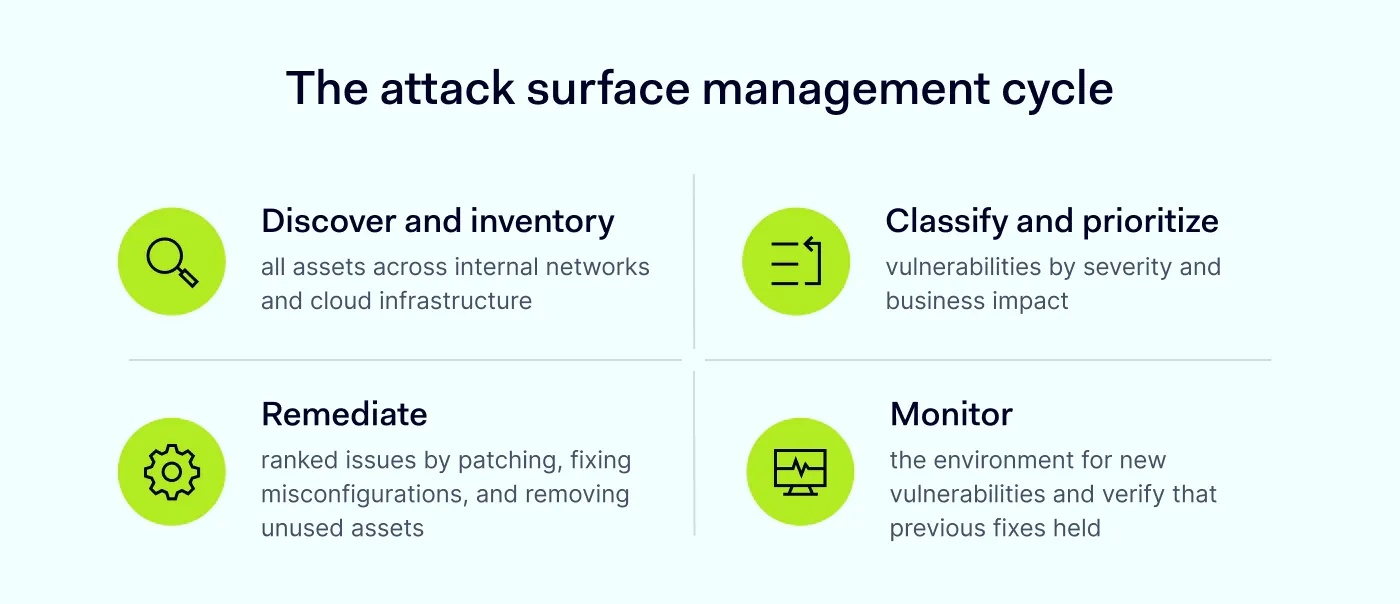
ASM consists of 4 core components that work in a repeating cycle. Each stage feeds the next, and monitoring returns to discovery as the environment changes.
Asset discovery and inventory. The first stage is a thorough scan to find every asset across the internal network and cloud infrastructure, including known systems, shadow IT, and rogue assets. Each asset can carry its own vulnerabilities, so full visibility is what every later stage depends on.
Classification and risk prioritization. Vulnerabilities carry different levels of risk, so the findings are triaged and ranked by severity and potential impact on the organization. This assessment tells security teams which exposures to address first and guides the remediation plan.
Remediation. Teams fix the ranked issues, starting with the most critical, by patching software, correcting misconfigurations, removing unused assets, and tightening access controls. At this stage, the surface shrinks.
Monitoring and validation. Attack surfaces change as assets join and leave the network, so monitoring runs as an ongoing process that flags new vulnerabilities as they appear and confirms that earlier fixes were effective. Fast discovery allows a fast response before an exposure is used, and each new finding resets the cycle to discovery.
Examples of attack surface management
An organization’s attack surface consists of all the assets exposed to potential cyber threats, including on-premises systems, cloud assets, internet-facing assets, and mobile devices. As an organization undergoes digital transformation, its attack surface grows and changes, introducing new attack vectors and cyber risks.
Let’s look at some concrete examples of attack surfaces and how malicious actors can exploit them:
Web applications. Web applications are a common attack vector, as they are often exposed to the public internet and can contain vulnerabilities that attackers can exploit to gain unauthorized access to sensitive data.
Cloud environments. Cloud environments introduce new cyber risks, such as misconfigured security settings, insecure APIs, and shared resources. Attackers can exploit these vulnerabilities to gain access to sensitive data or launch attacks on other cloud tenants
Third-party risks. Third-party vendors and partners can introduce new vulnerabilities to an organization’s network; for example, a vendor’s compromised system could provide attackers with a foothold in the organization’s network.
Remote access. Remote access solutions, such as VPNs and Remote Desktop Protocol (RDP), can be targeted by attackers to gain access to a company’s network.
IoT devices.Internet of Things (IoT) devices, such as security cameras and smart thermostats, can be vulnerable to attacks and provide attackers with a foothold in an organization’s network.
ASM vs. vulnerability management
ASM and vulnerability management overlap but answer different questions. ASM finds what you have and what you expose from the outside, while vulnerability management measures and fixes the weaknesses in the assets you already track. Most security programs run both, with ASM feeding newly discovered assets into the vulnerability management process.
Aspect
Attack surface management
Vulnerability management
Main question
What assets do we expose, and where?
Which known assets have exploitable flaws?
Starting point
Unknown and known assets, found from outside.
A defined inventory of known assets.
Viewpoint
Outside-in, from the attacker’s perspective.
Inside-out, across systems you already track.
Primary output
A current map of the exposed attack surface.
A ranked list of vulnerabilities to remediate.
Handles shadow IT
Yes, discovery is a core function.
Limited. Traditional VM focuses on known, in-scope assets, but some modern platforms also provide asset discovery.
Reducing your attack surface means removing exposure points and limiting what each remaining one can reach. A few measures deliver most of the reduction:
Apply zero-trust access. Verify every user and device before granting access, and grant only what each role needs, so one compromised account cannot reach the whole network.
Enforce least-privilege permissions. Give accounts, services, and APIs the minimum access required, and review permissions on a set schedule to remove ones no longer needed.
Secure remote access. Replace exposed remote access methods with controlled connections, and deny access from jailbroken or noncompliant devices.
Require strong authentication. Use multi-factor authentication (MFA) across accounts to make stolen credentials far less useful to an attacker.
Remove unused and unknown assets. Decommission old systems, retire deprecated APIs, and bring shadow IT under management so nothing stays online unmonitored.
Segment the network. Divide the network into separate zones to limit lateral movement and help contain a breach.
Keep protective backups. Maintain isolated, tested backups to support recovery if an attack succeeds.
Even a small enterprise can have an immense attack surface. Hackers can target internet-facing assets and may use vulnerabilities or misconfigurations in them to gain access to internal systems. Many attack surface management vendors promise that theirs is a one-click solution, but its implementation is a multi-step process.
Finding vulnerabilities and patching them up before an attacker does it helps to maintain the organization’s security. A strong vulnerability management program and ongoing cybersecurity vulnerability assessment can dramatically decrease risks.
How can NordLayer help?
NordLayer provides a security service edge, or SSE-focused network management solution, to address dynamic organizations' needs. It offers a complete overview of the company's network, allowing its segmentation into separate teams and gateways and minimizing the attack surface.
With NordLayer, you can deny connections from jailbroken devices to protect your network from potential risks. This can be incredibly beneficial for businesses by bringing their device policies, which usually have a large attack surface. It's a great starting point to control your internal network better and minimize business exposure to online threats.
Contact our team and discover more about our approach that could improve your organization's security status.
Attack surface management FAQ
Are there any attack surface management tools?
Yes, there are several commercial attack surface management solutions and platforms available from cybersecurity vendors. These tools are designed to help organizations automatically discover, monitor, and assess their entire external attack surface across internet-facing known and unknown assets.
These solutions use techniques like network scanning, code analysis, data mining, and threat intelligence to continuously map an organization's internet exposure across web apps, domains, IPs, code repositories, and more. They can detect unknown/rogue assets, monitor for misconfigured systems, and prioritize remediation based on risk.
How can an organization protect itself from cyberattacks?
Attack surface management can help organizations minimize risk and protect against possible attack vectors by providing continuous visibility and monitoring of internal and external assets in the organization's network. By identifying and prioritizing the remediation of known vulnerabilities and security gaps, organizations can minimize their attack surface visibility and protect against potential threats.
Security teams and threat intelligence can also provide an attack surface management solution to help security leaders decide where to focus their resources. Continuous discovery and penetration testing can also help identify new attack vectors and ensure that the organization's exposure management strategy is current.
What are the benefits of attack surface management?
Attack surface management (ASM) helps you see your organization like an attacker would. Its main benefits are:
Complete visibility: It discovers all your internet-facing assets, including forgotten systems and shadow IT, so you know what to protect.
Risk reduction: It identifies and prioritizes the most exposed vulnerabilities, letting you fix the most critical weaknesses first.
Greater efficiency: It automates the manual work of asset discovery and monitoring, saving your security team time and resources.
What challenges do organizations face with attack surface management?
A primary challenge is managing a constantly changing and expanding attack surface. With many operations now in the cloud, the traditional, fixed network perimeter no longer exists, making it difficult to monitor and secure a global network that lies beyond traditional firewalls. This surface also grows daily as new assets join the network, requiring automated strategies to secure publicly exposed assets.
Another significant challenge is organizational. Security teams are often siloed and geographically distributed across remote networks or multinational offices. This can hinder collaboration when trying to monitor and map the attack surface, making it difficult for teams to work together toward the common goal of threat prevention.
What’s the difference between an attack surface and a cyber threat?
An attack surface is the set of points or paths an attacker could target. A cyber threat is a circumstance, actor, or event with the potential to cause harm, while a cyberattack is an actual attempt to compromise a system.
What is external attack surface management?
The external attack surface refers specifically to the components exposed to the public internet—websites, servers, cloud infrastructure, and resources reachable from outside the corporate network. This area is most vulnerable to attack by external cyber threat actors. Robust cyberattack surface management and security operations are critical for preventing breaches, data exposure, and system compromises originating from internet-based attacks.
Joanna Krysińska
Senior Cybersecurity Copywriter
Joanna writes about zero trust, network security, access control, and threat prevention, but her cup of tea is compliance and how regulations shape security controls.
Her work also includes the dark web topics and the methods cybercriminals use to target companies, such as social engineering or ransomware attacks, for example.