
An information security management system (ISMS) is only as strong as the controls behind it. ISO/IEC 27001:2022 published by the International Organization for Standardization gives security teams 93 controls to choose from in Annex A when they design, operate, and audit an ISMS.
This guide covers what Annex A controls are, how the new 4-theme structure in the 2022 version replaced the previous 14 domains, the complete list of ISO 27001 controls, the 11 new additions in the 2022 version, and how to tie each control to a risk assessment and your Statement of Applicability (SoA).
What are ISO 27001 Annex A controls?
The ISO 27001 Annex A controls are a reference set of 93 ISO 27001 security controls that organizations draw from when treating identified risks in their ISMS. They are listed in Annex A of ISO/IEC 27001:2022 and described in detail in the companion standard, ISO/IEC 27002:2022.
Controls are not the same as clauses. Clauses 4–10 of ISO 27001 set out the mandatory requirements that organizations are audited against—things like context, leadership, planning, operation, and improvement. One of those requirements is to run a risk assessment and treat the risks it identifies The Annex A controls provide a menu of safeguards available for that treatment: applicable controls are implemented, and any that are left out are justified in the SoA.
Key takeaways
- ISO 27001 is a dynamic framework that mitigates information security risks. The latest version is ISO 27001:2022, which made several changes to the 2013 version.
- The core themes of ISO 27001:2022 are organizational, people, physical, and technological controls. The 2022 version introduces a greater focus on planning and interested parties, while simplifying the list of recommended controls. However, the register of controls remains relevant and guides companies as they achieve ISO compliance.
- Annex A is the core register of ISO controls. This list of controls has 4 themes, covering 93 controls in total. These themes address major information security topics, including technical, physical, human, and operational security. They span supplier relationships, incident response and change management.
- Organizations should take a risk-based approach to the implementation of ISO 27001. Planners should consider the business context. They should select controls that mitigate real-world security risks and audit their ISO 27001 implementation to ensure compliance.
ISO 27001:2022 Annex A structure
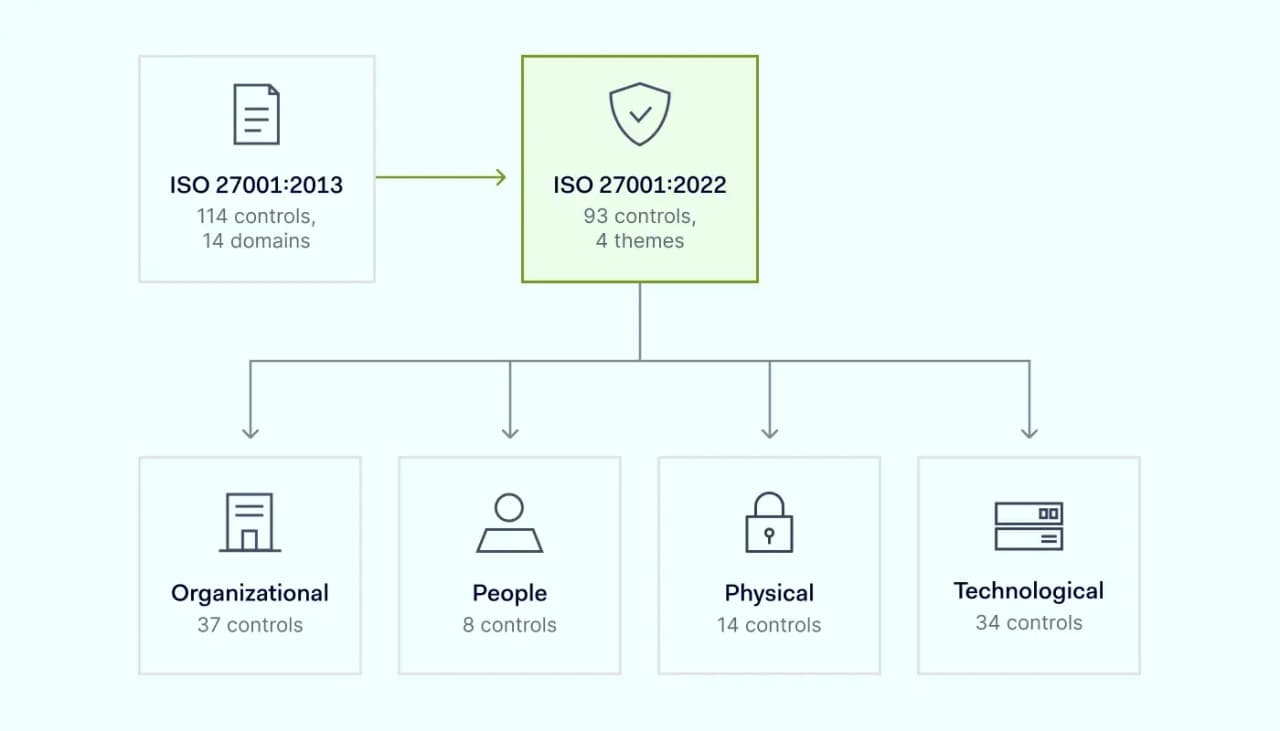
The ISO 27001:2022 standard groups Annex A controls into 4 themes, replacing the 14 ISO 27001 domains used in the 2013 version. The themes reflect what the control governs rather than the technical discipline it belongs to, which makes the set easier to apply across different company sizes and industries.
Theme | Clause range | Controls | Focus |
|---|---|---|---|
Organizational | 5.1–5.37 | 37 | Policies, roles and responsibilities, information asset management, supplier and cloud relationships, incident management, regulatory compliance |
People | 6.1–6.8 | 8 | Screening, employment terms, awareness, disciplinary processes, remote work, reporting channels |
Physical | 7.1–7.14 | 14 | Secure areas, equipment, cabling, clear desks and screens, media disposal |
Technological | 8.1–8.34 | 34 | Access control, cryptography, change management, configuration management, malware protection, backup management, logging and monitoring, secure development |
Compared to the 2013 version, ISO 27001:2022 merges 57 of the previous 114 controls into 24, adds 11 new ones, and ends up with 93 controls total No controls were deleted outright—most of the old requirements are still there, just reorganized.
Full list of ISO 27001:2022 Annex A controls (all 93)
The full list of ISO/IEC 27001:2022 Annex A controls is below, split into 4 tables—one per theme—with a one-line purpose statement for each control. New controls added in 2022 are flagged.
Theme 5: organizational controls (37)
ID | Control name | Purpose |
|---|---|---|
5.1 | Policies for information security | Define, approve, publish, and review information security policies |
5.2 | Information security roles and responsibilities | Allocate and communicate security responsibilities across the organization |
5.3 | Segregation of duties | Separate conflicting duties to reduce fraud, errors, and misuse |
5.4 | Management responsibilities | Require personnel to apply security measures per approved policies |
5.5 | Contact with authorities | Keep defined contact with regulators and law enforcement |
5.6 | Contact with special interest groups | Maintain links with security forums and professional associations |
5.7 | Threat intelligence | (New) Collect and analyze threat intelligence to inform decisions |
5.8 | Information security in project management | Integrate information security into every project |
5.9 | Inventory of information and other associated assets | Maintain an asset inventory (hardware and software) with owners |
5.10 | Acceptable use of information and other associated assets | Document and apply acceptable-use rules |
5.11 | Return of assets | Recover assets when employment or contracts end |
5.12 | Classification of information | Classify information by confidentiality, integrity, and availability |
5.13 | Labelling of information | Apply handling labels based on the classification scheme |
5.14 | Information transfer | Secure transfers across electronic, physical, and verbal channels |
5.15 | Access control | Establish rules for physical and logical access |
5.16 | Identity management | Manage the full identity lifecycle |
5.17 | Authentication information | Control the issue, storage, and change of secrets |
5.18 | Access rights | Provision, review, modify, and remove access rights |
5.19 | Information security in supplier relationships | Define security requirements for supplier products and services |
5.20 | Addressing information security within supplier agreements | Build security requirements into supplier contracts |
5.21 | Managing information security in the ICT supply chain | Manage ICT product and service supply chain risk |
5.22 | Monitoring, review, and change management of supplier services | Monitor and review supplier security over time |
5.23 | Information security for use of cloud services | (New) Govern acquisition, use, and exit from cloud services |
5.24 | Information security incident management planning and preparation | Plan and prepare for incident response |
5.25 | Assessment and decision on information security events | Evaluate events and decide whether to treat them as incidents |
5.26 | Response to information security incidents | Respond per documented procedures |
5.27 | Learning from information security incidents | Use lessons learned to reduce future risk |
5.28 | Collection of evidence | Collect and preserve evidence for investigations |
5.29 | Information security during disruption | Keep information secure during disruption |
5.30 | ICT readiness for business continuity | (New) Plan, implement, and test ICT continuity |
5.31 | Legal, statutory, regulatory, and contractual requirements | Identify and maintain compliance requirements |
5.32 | Intellectual property rights | Protect intellectual property |
5.33 | Protection of records | Protect records from loss, destruction, falsification, and unauthorized access |
5.34 | Privacy and protection of PII | Meet privacy and PII protection obligations |
5.35 | Independent review of information security | Review the ISMS independently at planned intervals |
5.36 | Compliance with policies, rules, and standards | Review compliance with policies and standards |
5.37 | Documented operating procedures | Document operating procedures and make them available |
Theme 6: people controls (8)
ID | Control name | Purpose |
|---|---|---|
6.1 | Screening | Verify candidates per laws, regulations, and ethics |
6.2 | Terms and conditions of employment | State security responsibilities in employment terms |
6.3 | Information security awareness, education, and training | Give personnel appropriate awareness and training |
6.4 | Disciplinary process | Formalize and communicate a disciplinary process |
6.5 | Responsibilities after termination or change of employment | Keep security obligations in force after a role change |
6.6 | Confidentiality or non-disclosure agreements | Identify, document, review, and sign NDAs |
6.7 | Remote working | Apply security measures for remote work |
6.8 | Information security event reporting | Give staff a clear mechanism to report suspected security events |
Theme 7: physical controls (14)
ID | Control name | Purpose |
|---|---|---|
7.1 | Physical security perimeters | Define perimeters that protect facilities and information |
7.2 | Physical entry | Control entry to secure areas |
7.3 | Securing offices, rooms, and facilities | Apply physical security to offices and facilities |
7.4 | Physical security monitoring | (New) Monitor premises continuously for unauthorized access |
7.5 | Protecting against physical and environmental threats | Guard against natural and deliberate physical threats |
7.6 | Working in secure areas | Define measures for working in secure areas |
7.7 | Clear desk and clear screen | Enforce clear-desk rules for papers, media, and screens |
7.8 | Equipment siting and protection | Site equipment to reduce environmental risk |
7.9 | Security of assets off-premises | Protect assets used outside the office |
7.10 | Storage media | Manage media through its full lifecycle |
7.11 | Supporting utilities | Protect against power and utility failures |
7.12 | Cabling security | Protect power and communications cabling |
7.13 | Equipment maintenance | Maintain equipment for availability and integrity |
7.14 | Secure disposal or reuse of equipment | Verify sensitive data is removed before disposal or reuse |
Theme 8: technological controls (34)
ID | Control name | Purpose |
|---|---|---|
8.1 | User endpoint devices | Secure endpoint devices through policy and technical measures |
8.2 | Privileged access rights | Restrict and manage privileged access |
8.3 | Information access restriction | Restrict access per access control policy |
8.4 | Access to source code | Restrict read and write access to source code |
8.5 | Secure authentication | Implement authentication aligned to access restrictions |
8.6 | Capacity management | Monitor and adjust resource capacity |
8.7 | Protection against malware | Protect systems and endpoints against malware |
8.8 | Management of technical vulnerabilities | Identify and remediate vulnerabilities on time |
8.9 | Configuration management | (New) Establish, document, monitor, and review configurations |
8.10 | Information deletion | (New) Delete information when it is no longer needed |
8.11 | Data masking | (New) Mask data per access and business or legal requirements |
8.13 | Data leakage prevention | (New) Apply DLP across systems, networks, and endpoints |
8.13 | Information backup | Maintain and test backups per policy |
8.14 | Redundancy of information processing facilities | Build in enough redundancy to meet availability needs |
8.15 | Logging | Produce and store logs of activities, exceptions, and events |
8.16 | Monitoring activities | (New) Monitor networks, systems, and applications for anomalies |
8.17 | Clock synchronization | Synchronize clocks to approved time sources |
8.18 | Use of privileged utility programs | Restrict programs that can override controls |
8.19 | Installation of software on operational systems | Manage software installation on production systems |
8.20 | Networks security | Secure and manage networks and network devices |
8.21 | Security of network services | Identify security features and service levels of network services |
8.22 | Segregation of networks | Segregate services, users, and systems in the network |
8.23 | Web filtering | (New) Manage access to external websites to reduce malware exposure |
8.24 | Use of cryptography | Define and apply rules for cryptography |
8.25 | Secure development life cycle | Define rules for secure development |
8.26 | Application security requirements | Specify and document security requirements for applications |
8.27 | Secure system architecture and engineering principles | Apply secure engineering principles |
8.28 | Secure coding | (New) Apply secure coding principles in development |
8.29 | Security testing in development and acceptance | Define and run security testing in the SDLC |
8.30 | Outsourced development | Supervise and monitor outsourced development |
8.31 | Separation of development, test, and production environments | Separate and secure environments |
8.32 | Change management | Manage changes to facilities and systems |
8.33 | Test information | Select and protect test information |
8.34 | Protection of information systems during audit testing | Plan audit tests to minimize operational disruption |
The 11 new controls in ISO 27001:2022
Compared with the 2013 edition, the ISO 27001:2022 controls set adds 11 brand-new entries. They reflect threats and practices that either didn’t exist or weren’t yet well understood when the previous version was published: cloud services, supply chain compromises, misconfiguration as a primary attack vector, and the increased risk of data leakage from distributed workforces.
New control | Name | Theme | Why it was added |
|---|---|---|---|
5.7 | Threat intelligence | Organizational | Formal intelligence collection replaced reactive security |
5.23 | Information security for use of cloud services | Organizational | Cloud adoption outpaced the 2013 coverage |
5.30 | ICT readiness for business continuity | Organizational | Separates ICT continuity from general business continuity |
7.4 | Physical security monitoring | Physical | Continuous monitoring, not just periodic access-log review |
8.9 | Configuration management | Technological | Misconfiguration is now a top cause of breaches |
8.10 | Information deletion | Technological | Data minimization and retention compliance tightened |
8.11 | Data masking | Technological | Privacy laws (GDPR, HIPAA, CCPA) raised masking expectations |
8.12 | Data leakage prevention | Technological | Insider risk and exfiltration grew sharply |
8.16 | Monitoring activities | Technological | Behavioral monitoring and SIEM formalized as their own control |
8.23 | Web filtering | Technological | Browser-based attacks became the dominant endpoint entry |
8.28 | Secure coding | Technological | Software supply chain and OWASP-class issues demanded formal cover |
Beyond the new controls, the 2022 revision also tightens a few requirements in the main clauses: Clause 4.2 now explicitly asks you to consider what interested parties expect from your ISMS, Clause 6 puts more weight on documented information security objectives and planned changes to the ISMS, and Clause 7.4 sharpens the expectation to make sure security roles are clearly communicated across the business.
The transition period for 2013 certificates ended on October 31, 2025. Any organization still with a 2013 certificate should get in touch with its certification body because recertification is now a new audit, not a transition
Are Annex A controls required?
At first glance, Annex A can read like a mandatory ISO 27001 controls checklist, but it isn’t. Companies tend to pick the controls that fit their information security systems and risk profile, so very few of them apply all 93.
Whether a company implements an ISO 27001 control depends on its risk profile. For example, companies without remote workers won’t need to worry about securing remote devices.
However, organizations must apply controls when risk assessments recommend it. ISO 27001 is a risk-based security framework. Companies that fail to act on identified security risks will likely fail their certification audits.
Deciding which ISO 27001 controls to implement
Determining the scope of ISO 27001 implementation is critically important. As a rule, the ISMS should be as simple as possible. Controls should only apply when they mitigate serious risks. The core challenge is deciding which risks apply and classifying those risks to determine relevant controls.
The context of the organization is all-important. For example, healthcare companies face critical risks around patient privacy, data portability, cybersecurity, and vendor relationships. Companies that want to achieve HIPAA compliance must apply many ISO 27001 controls.
The risks differ for eCommerce businesses that handle financial data and little else. A cloud-based online seller may need to apply network security controls, access management, and personnel management. However, other areas of the ISO 27001 framework are less relevant.
The risk assessment determines the mix of controls for each situation. Assess your business operations. Compare your information security systems against ISO controls, and apply controls that help to protect your sensitive data.
Who is responsible for the implementation of ISO 27001 controls?
ISO 27001 implementation is usually run by a separate team within the organization. Companies typically do not use their computer security incident response team (CSIRT) for this task—incident responders have a different role, and pulling them into a certification project burns the capacity you need for actual incidents. The governance, risk, and compliance (GRC) or information security team that owns the implementation should be independent of the people operating the ISMS day to day, although drawing on internal technical expertise is essential.
Organizations should start by appointing a dedicated information security lead. This individual should then bring together team leads from different parts of the organization. Specific areas of expertise to recruit include:
- Legal or compliance officers. To draft compliant policies relating to ISO 27001 controls.
- HR officers. To implement training, candidate vetting, and enforce staff responsibilities.
- IT technicians. To advise on technological controls and implement recommendations arising from the ISO 27001 process.
The information security team should also have backing at the executive level. Board members should participate in the process and assist the team at every stage.
If necessary, companies can bring in external contractors to manage the process. External expertise helps to deal with internal skill gaps and brings a fresh perspective to reforming information security systems.
Implementing ISO 27001 controls
With the 2022 structure, the new controls, and the transition deadline behind us, the practical question is how to put Annex A to work. The implementation process for achieving ISO 27001 compliance varies. But generally, the implementation process has the following components:
- Start by evaluating your organizational context: what you do, who your customers and regulators are, where your data is stored, and which Annex A controls are relevant to that picture (and which clearly aren’t).
- Catalog your existing information security policies, procedures, and controls.
- Execute risk assessments for information processing systems and core organizational workflows. Identify security risks and classify risks according to probability and severity.
- Compare ISO 27001 controls to the risk assessment. Which controls are needed to mitigate risks and create a secure Information Security Management System?
- Create an ISO 27001 implementation plan informed by the risk assessment. Ensure that the risk treatment plan covers every applicable ISO 27001 control.
- Carry out an internal audit to verify that ISO 27001 controls are in place. Ensure that corrective actions fix any gaps.
Build a risk-based ISO 27001 program
This article has explored the role of ISO 27001 controls in building secure information processing systems. ISO 27001 Annex A is a comprehensive framework with many sub-annexes and recommended controls. However, companies can adopt these controls to suit their security needs.
Use risk-based analysis to identify ISO 27001 controls that will strengthen your information processing operation. Implement technical controls, policies, and procedures to protect critical data and enable ISO certification.
Disclaimer: This article is for informational purposes only and not legal advice. Use it at your own risk and consider consulting a licensed professional for legal matters. Content may not be up-to-date or applicable to your jurisdiction and is subject to change without notice.