Integrate NordLayer with CrowdStrike to detect threats faster
Bring NordLayer activity logs into the CrowdStrike Falcon® Next-Gen SIEM to view all security events in one place and cut the time it takes to identify risks.

14-day money-back guarantee
overview
How NordLayer and CrowdStrike work together for stronger security
A Zero Trust approach lives by the ‘trust-none, verify all’ mantra — ensuring every user, device, and connection is authenticated ahead of being granted access to your business network and its most valuable assets and sensitive data.
By integrating NordLayer with CrowdStrike Falcon® Next-Gen SIEM, your team gains a clearer, more complete view of endpoint and network access events on one platform.
With NordLayer activity logs appearing in the CrowdStrike SIEM solution alongside other threat indicators, you can identify suspicious activity and investigate anomalies more effectively. It also makes it easier to monitor user behavior and prioritize risks.
BENEFITS
Here’s what you gain from NordLayer + CrowdStrike

A comprehensive view of threats in a single console
See NordLayer activity logs directly in the CrowdStrike SIEM platform to avoid switching between tools and streamline threat investigations.

Faster detection of access-related risks
Correlate NordLayer admin actions and user connection data with the CrowdStrike next-gen SIEM solution to identify network access risks faster.

More actionable context on user behavior
Gain clear insights into user sessions, devices, and access changes to better understand potential risks and improve the accuracy of your threat response.

Automated instant logouts when a threat is detected
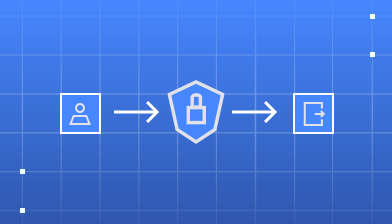
Ensure all affected NordLayer users are automatically logged out and disconnected from all gateways when CrowdStrike detects a security event.
Boost threat detection with NordLayer + CrowdStrike
RESOURCES
Learn more about NordLayer integrations
help center
CrowdStrike integration with NordLayer
CYBERSECURITY LEARNING CENTER