AI security for legal and infosec teams
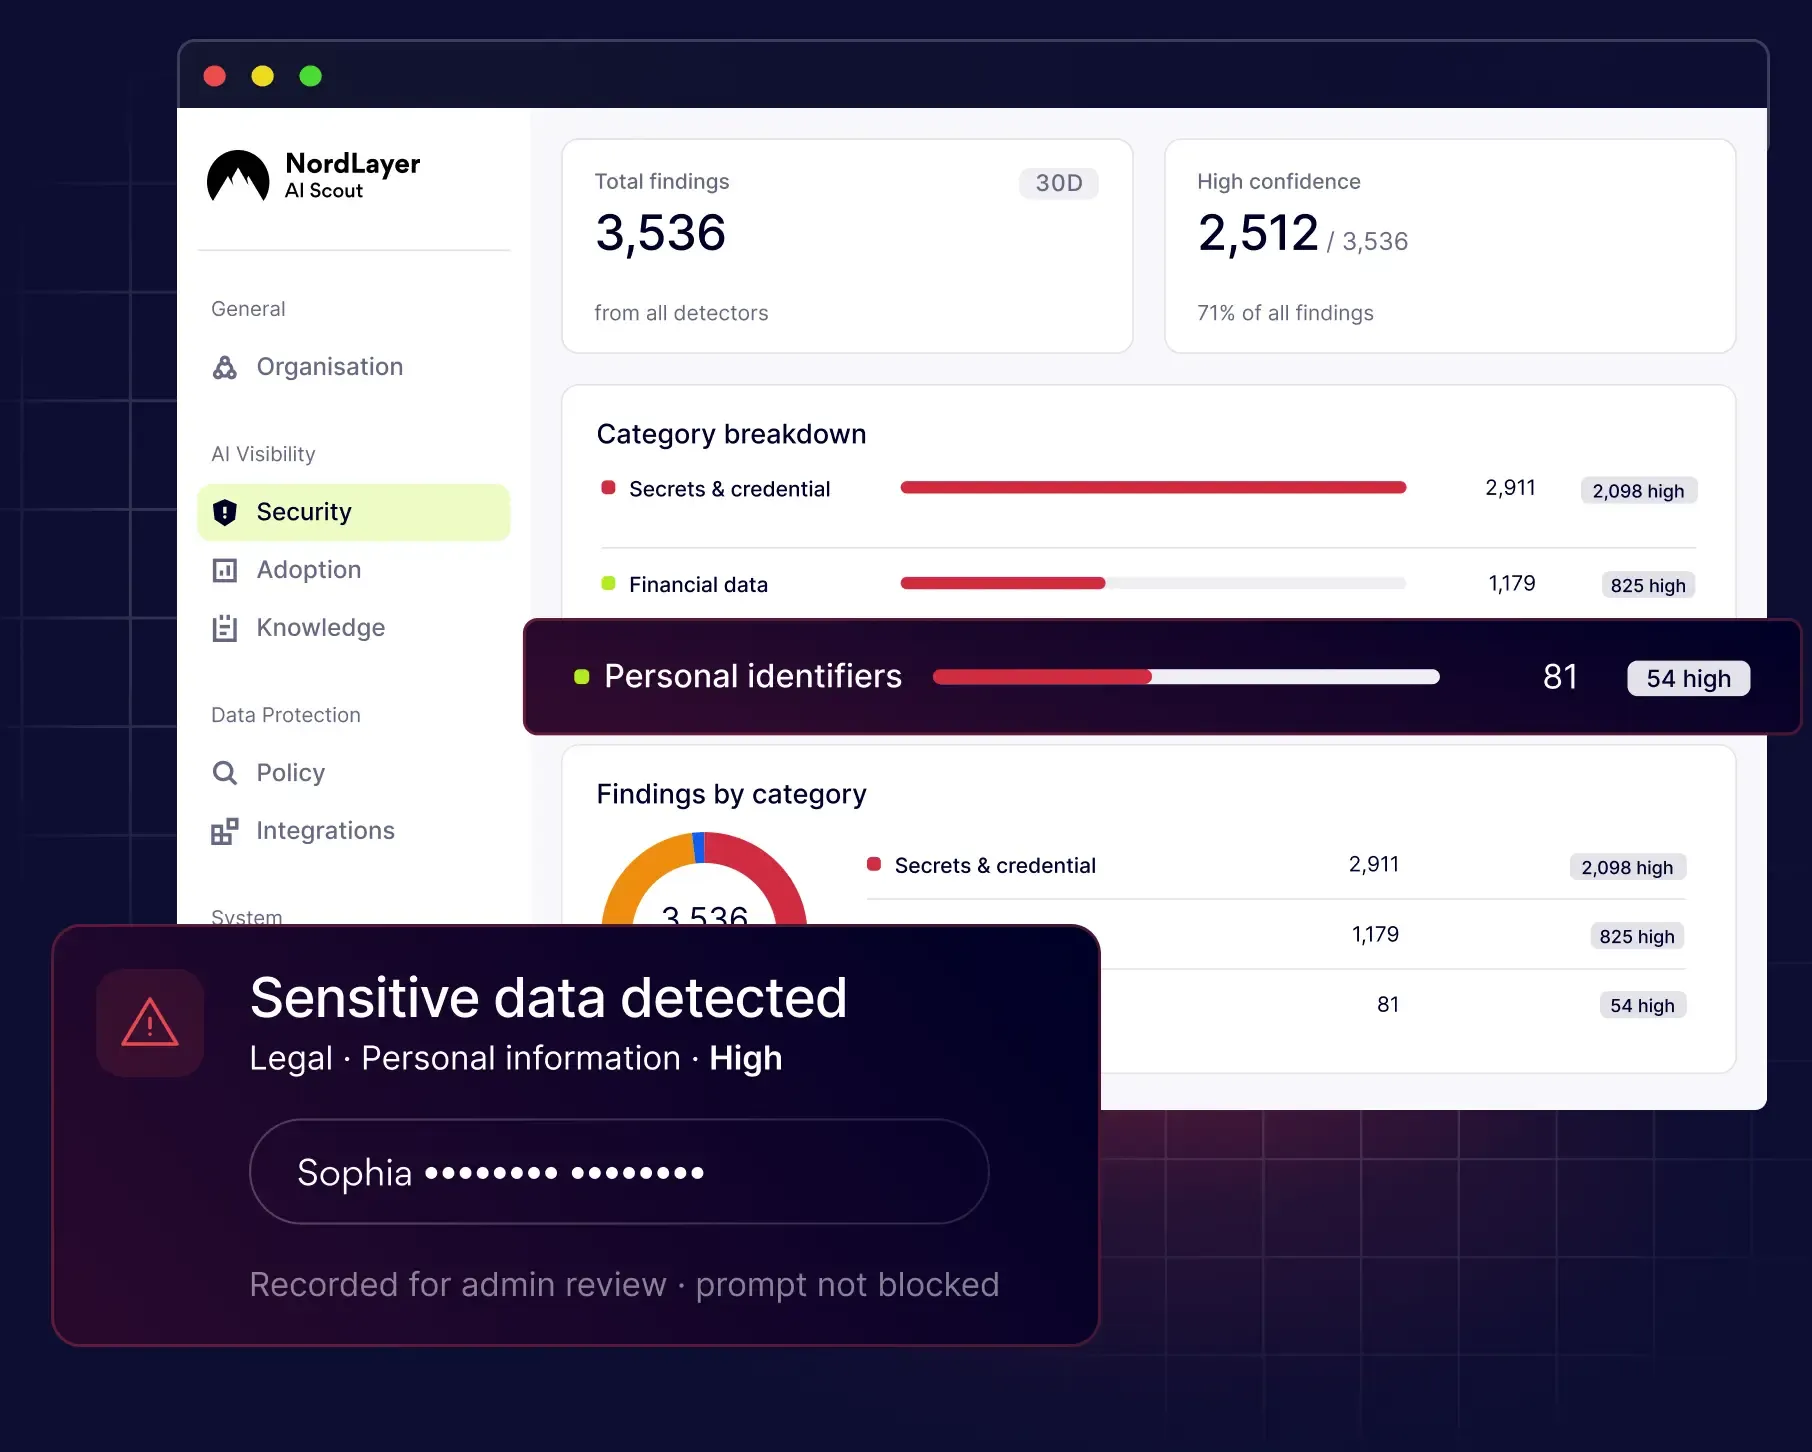
When a customer questionnaire, audit, or regulatory review asks how your organization uses and governs AI, show the evidence. NordLayer AI Scout gives you a searchable audit trail of AI activity and governance, so you can prove what happened, when, and under which policies.

Try every feature risk-free for 30 days
Statistics
The gap between AI use and oversight
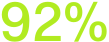
Access control made simple 92% of legal professionals now use at least one AI tool.
Source: Wolters Kluwer
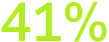
Access control made simple 41% of legal departments have never audited for unauthorized shadow AI use.
Source: The Association of Corporate Counsel
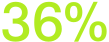
Access control made simple 36% of corporate legal, tax, and compliance professionals use AI tools their employer hasn’t authorized.
Source: Thomson Reuters Institute
KEY CHALLENGES
When AI use and decisions need to be explained
Legal teams are often brought in when someone needs proof: a customer security questionnaire, regulatory review, internal investigation, or governance check. The challenge is not just having AI policies in place. It’s being able to show who used which AI tools, what was shared, what rules applied, and how those rules changed over time.

Customers need evidence, not policy language
Customers increasingly ask how AI is used, monitored, and governed. Policies can explain the rules, but they do not prove what actually happened. Without a searchable record of AI activity, legal and security teams may struggle to back up their answers with evidence.

AI use can happen outside of approved processes
Employees might use unapproved AI tools, personal accounts, or AI features embedded in everyday applications. Without a record of this activity, the legal department may have no reliable way to reconstruct what was used, by whom, or what information was shared.

AI policies and decisions need a history
AI policies and settings change as tools, risks, and internal rules evolve. If someone questions a decision months later, the current policy may not explain what was in place at the time. Keeping a clear record of everything helps the legal team understand what changed and when.

Balancing AI records with employee privacy
Legal teams need records to review AI use and investigate issues. But keeping too much information can raise privacy concerns, while keeping too little may leave them without the evidence they need.

AI investigations take time
When an AI-related issue needs investigating, information may be scattered across different tools and logs. This can cause the legal, security, and privacy teams to waste time piecing together what happened. Keeping AI activity records in one place makes it easier to review the facts.

Regulatory reviews raise questions about AI use
Requirements such as the GDPR, the EU AI Act, and the DORA can bring questions about data handling, oversight, and accountability. Legal teams need a clear record of AI activity and governance decisions they can reference when regulators or auditors ask how controls were applied in practice.
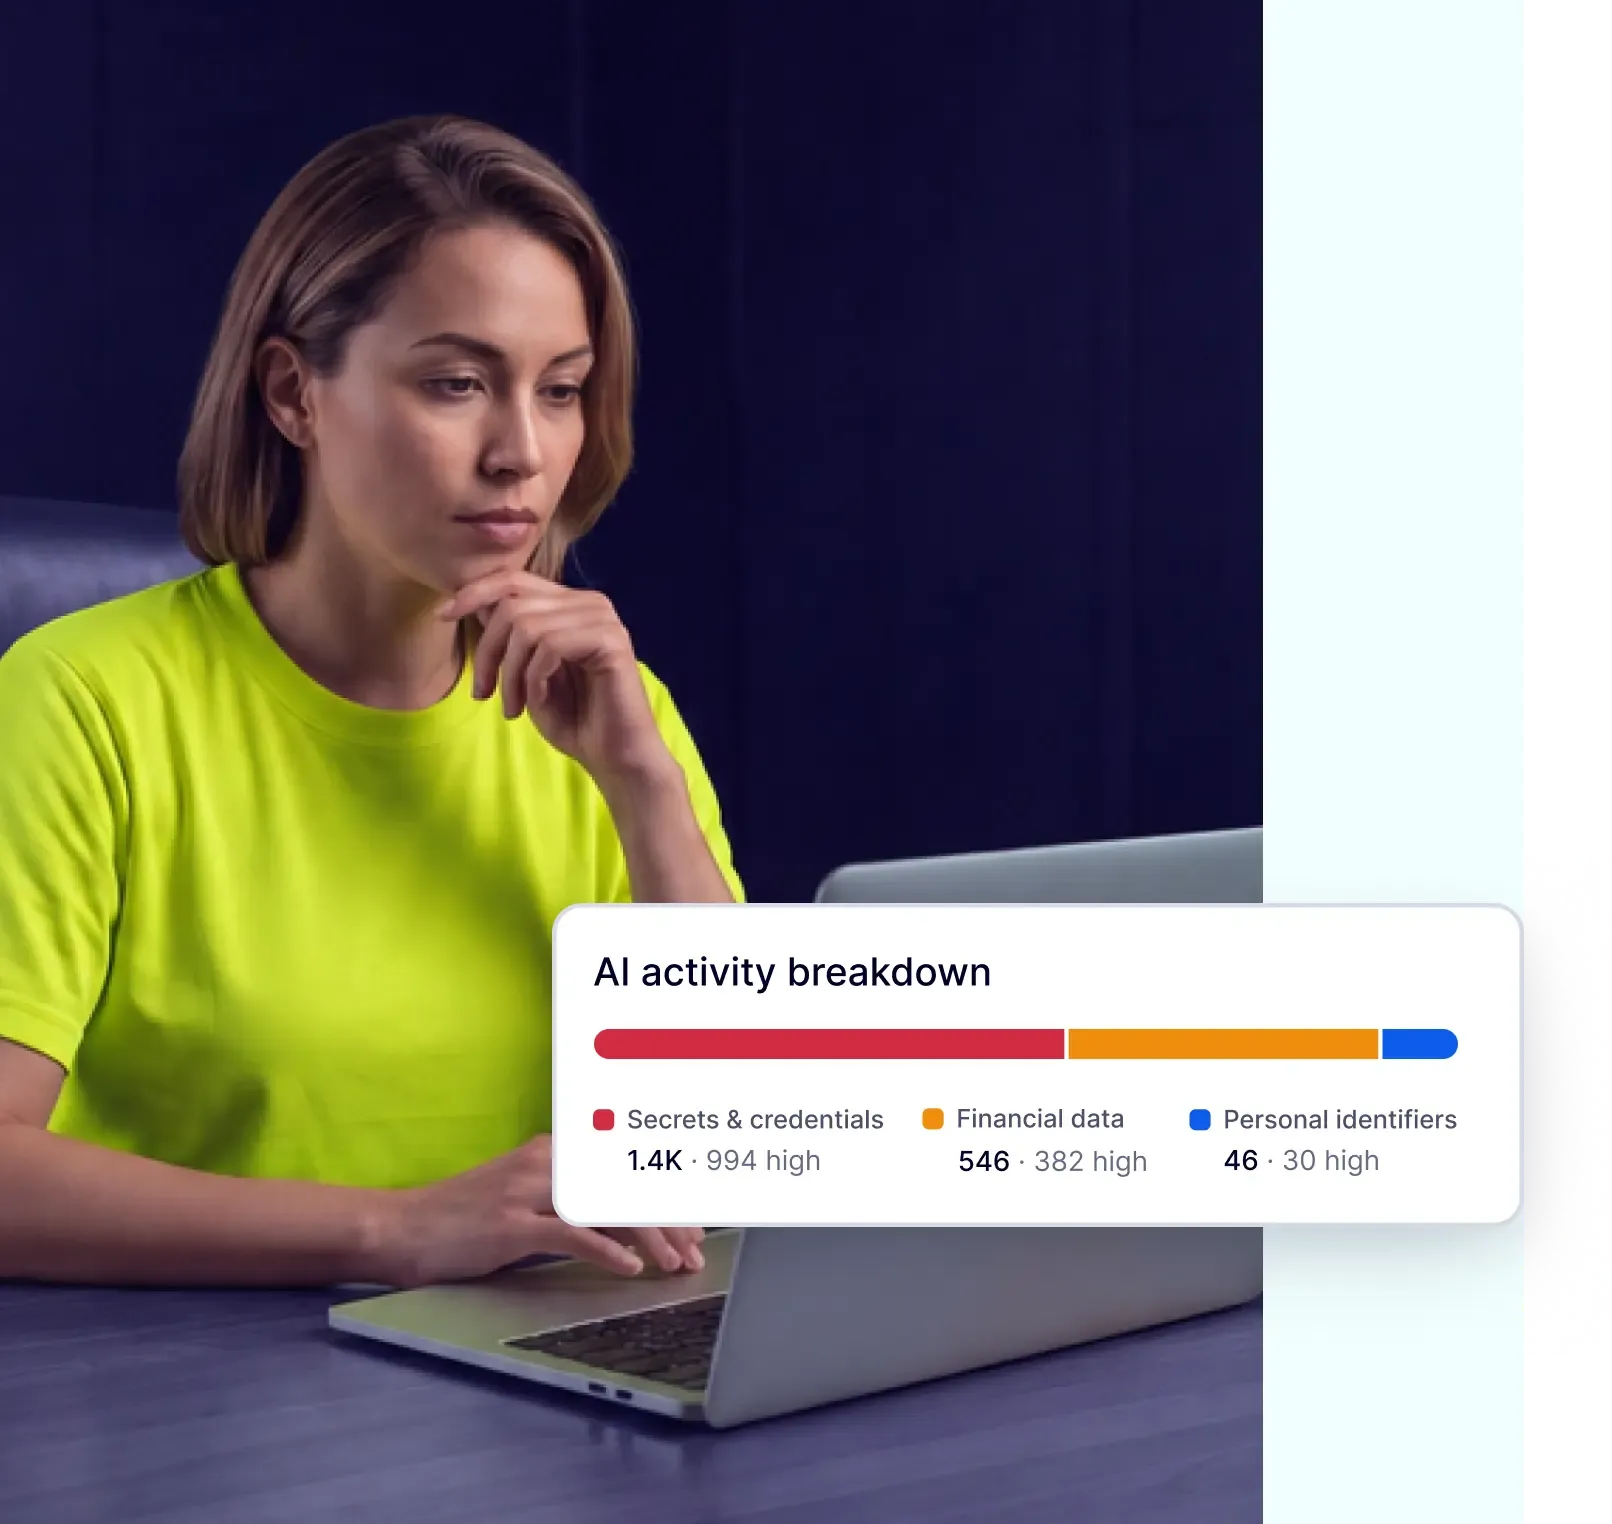
Build an AI audit trail you can stand behind
NordLayer AI Scout gives legal and infosec teams a searchable record of AI activity, policy changes, and governance decisions. Be ready with evidence when a customer, auditor, or regulator asks how AI is used and managed.
KEY ADVANTAGES
What NordLayer AI Scout offers legal and infosec teams
Be ready for the next questionnaire, audit, or internal review with evidence that is easy to find, understand, and export.
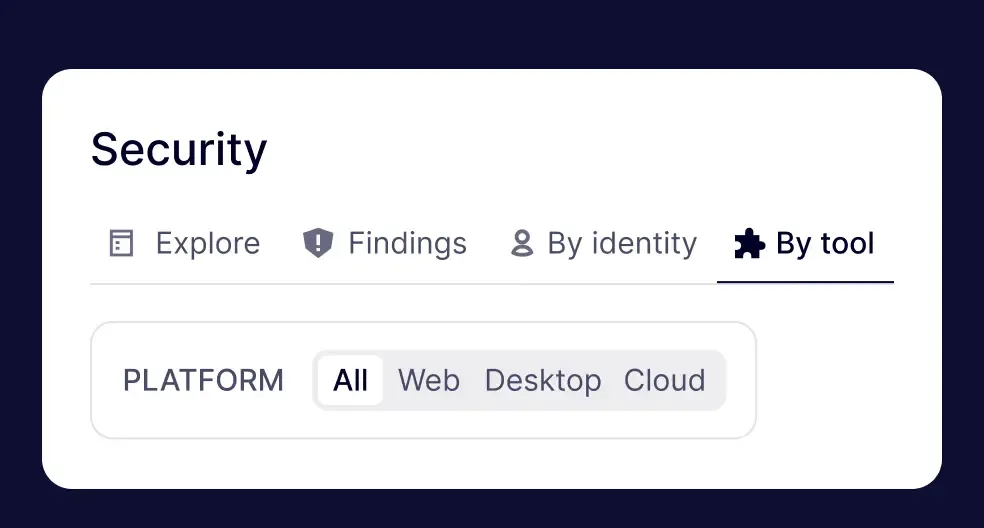
Have a searchable AI audit trail
Find recorded AI activity across the web and desktop by user, department, tool, and other available contexts.
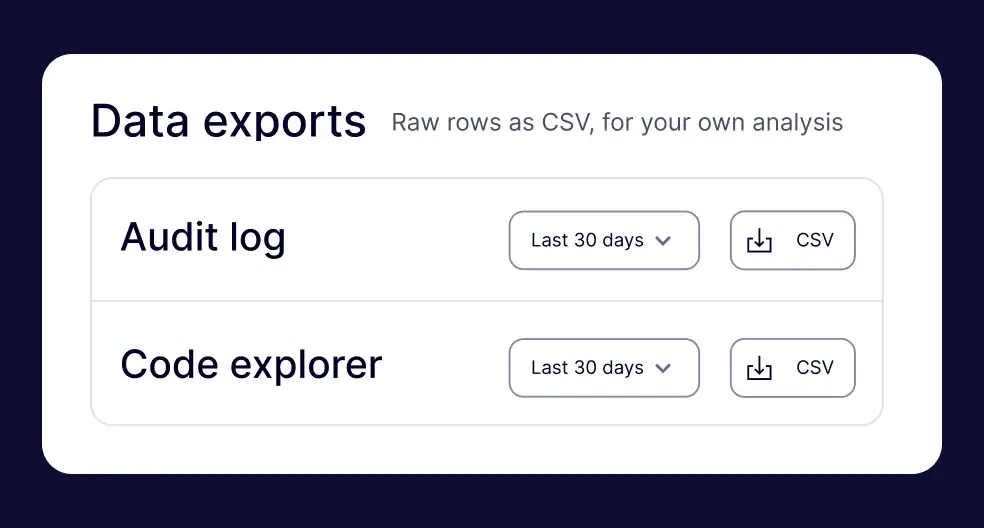
Export evidence on demand
Export relevant activity when you need supporting evidence for questionnaires, audits, regulatory reviews, or internal checks.
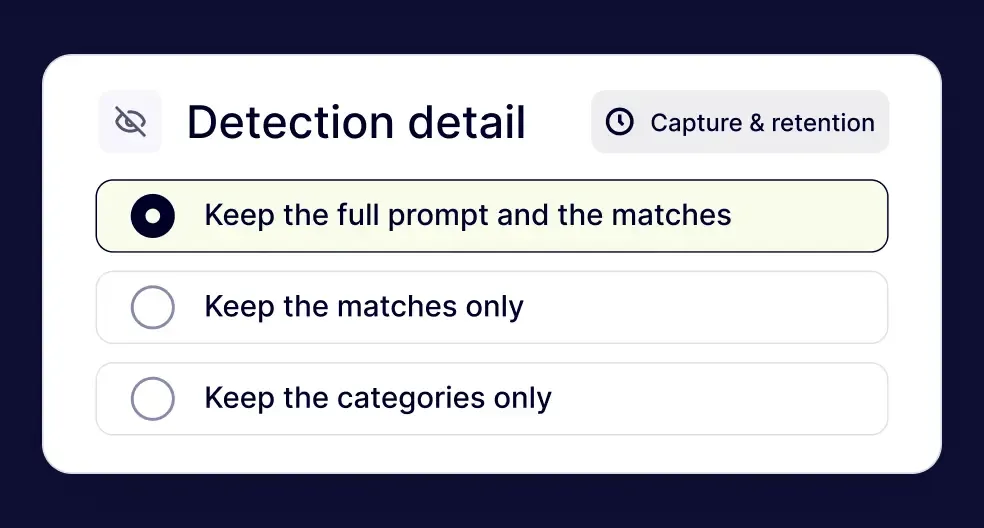
Control what data is retained
Choose what to keep: full prompts and detections, detections only, or categories only. Meet evidence needs without collecting unnecessary data.
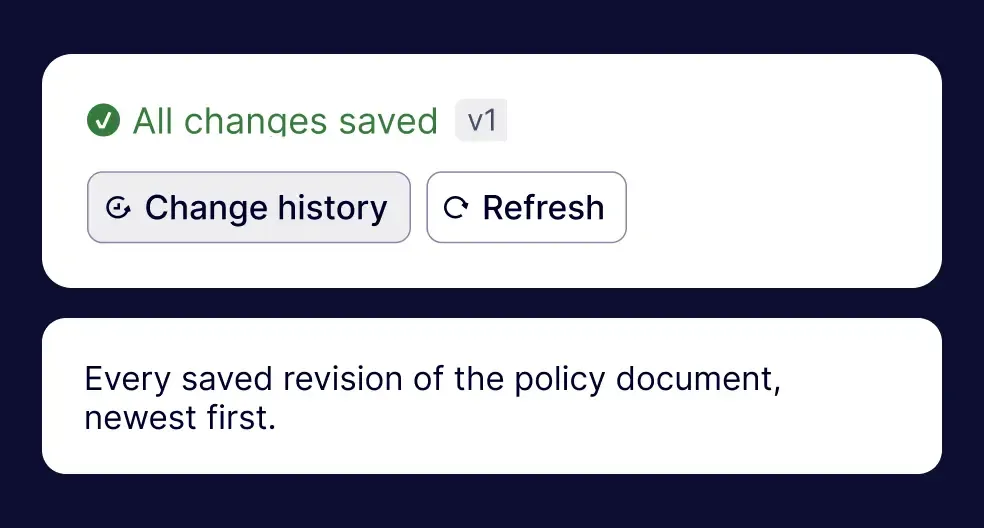
Track policy changes
Keep a record of policy and configuration changes alongside AI activity to show how AI use was managed over time.
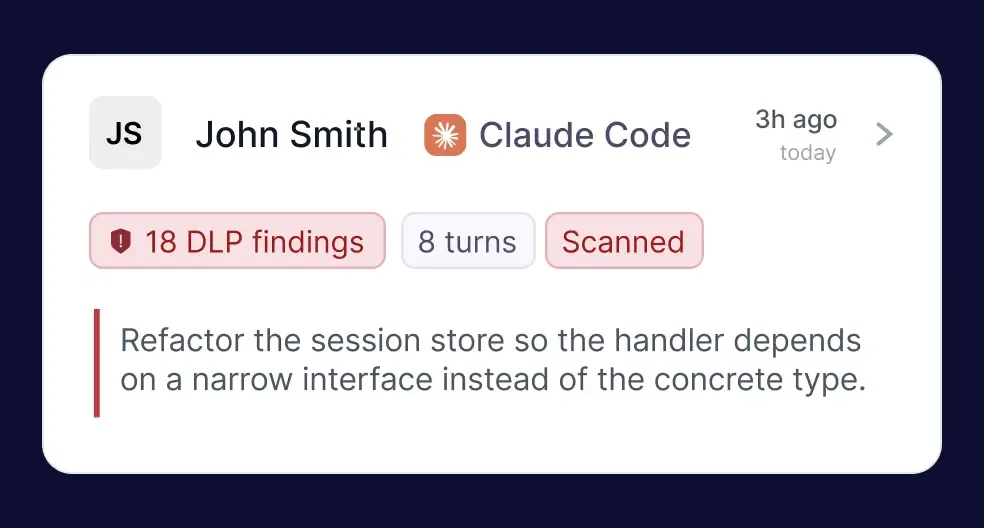
Speed up internal reviews
Review past AI activity in one place, so you can quickly find the evidence needed without pulling records from multiple systems.
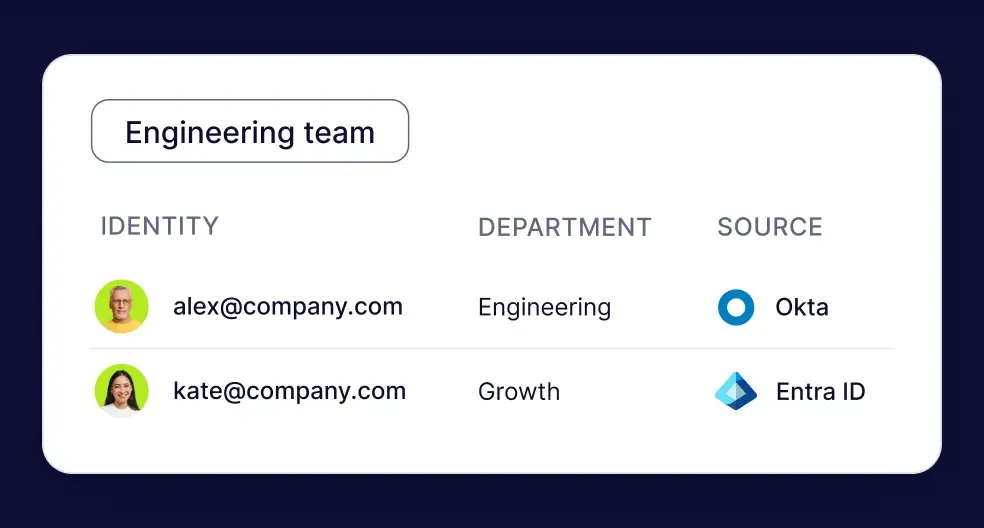
Understand AI use by user and team
Connect AI activity to users and teams, making it easier to understand who used which tools and where the activity occurred.
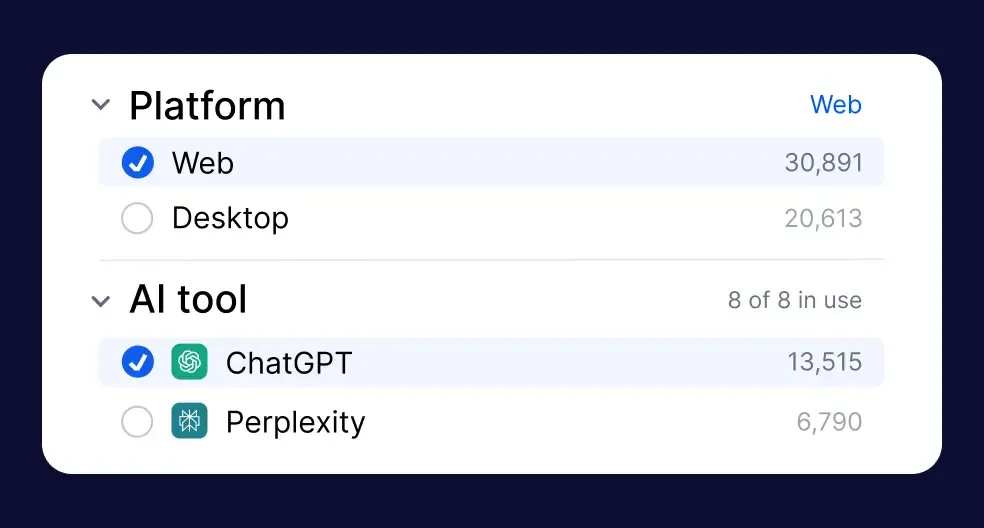
Cover web and desktop visibility
Capture AI activity across browser-based tools, desktop apps, and supported local AI agents – all from a single Control Panel.
MORE FOR YOUR ORGANIZATION
Explore AI security use cases for other teams


KNOWLEDGE HUB
Learn more about AI security best practices
CYBERSECURITY LEARNING CENTER
What is AI compliance?
CYBERSECURITY LEARNING CENTER
What is AI data leakeage?
CYBERSECURITY LEARNING CENTER
What is AI governance?
CYBERSECURITY LEARNING CENTER
Guide to NIST AI Risk Management Framework (AI RMF)
CYBERSECURITY LEARNING CENTER