Secure AI coding agents on every developer device
Get an AI coding agent security solution that reconstructs every coding session, from prompts to tool calls, and alerts you whenever company secrets, keys, or source code are mentioned.

Try every feature risk-free for 30 days
15,000+ businesses trust NordLayer to stay secure, compliant, and in control



THE CHALLENGE
AI coding has outpaced the controls meant to govern it
Developers are shipping code with AI agents that security teams rarely see, and when something goes wrong, few organizations can show what happened or what data left the device.
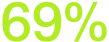
69% of security leaders say their organization suspects or has evidence of staff using prohibited public GenAI tools.
Source: Gartner
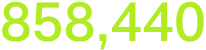
Source code is the most frequently exposed data type in GenAI tools, across 858,440 GenAI-related DLP events.
Source: Verizon 2026 DBIR
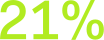
21% of companies report a mature governance model for their autonomous AI agents, even as most plan to deploy them.
Source: Deloitte_Italic_
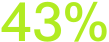
Only 43% are confident their organization could investigate a serious AI incident and explain it to leadership or regulators.
Source: ISACA
HOW NORDLAYER AI SCOUT HELPS
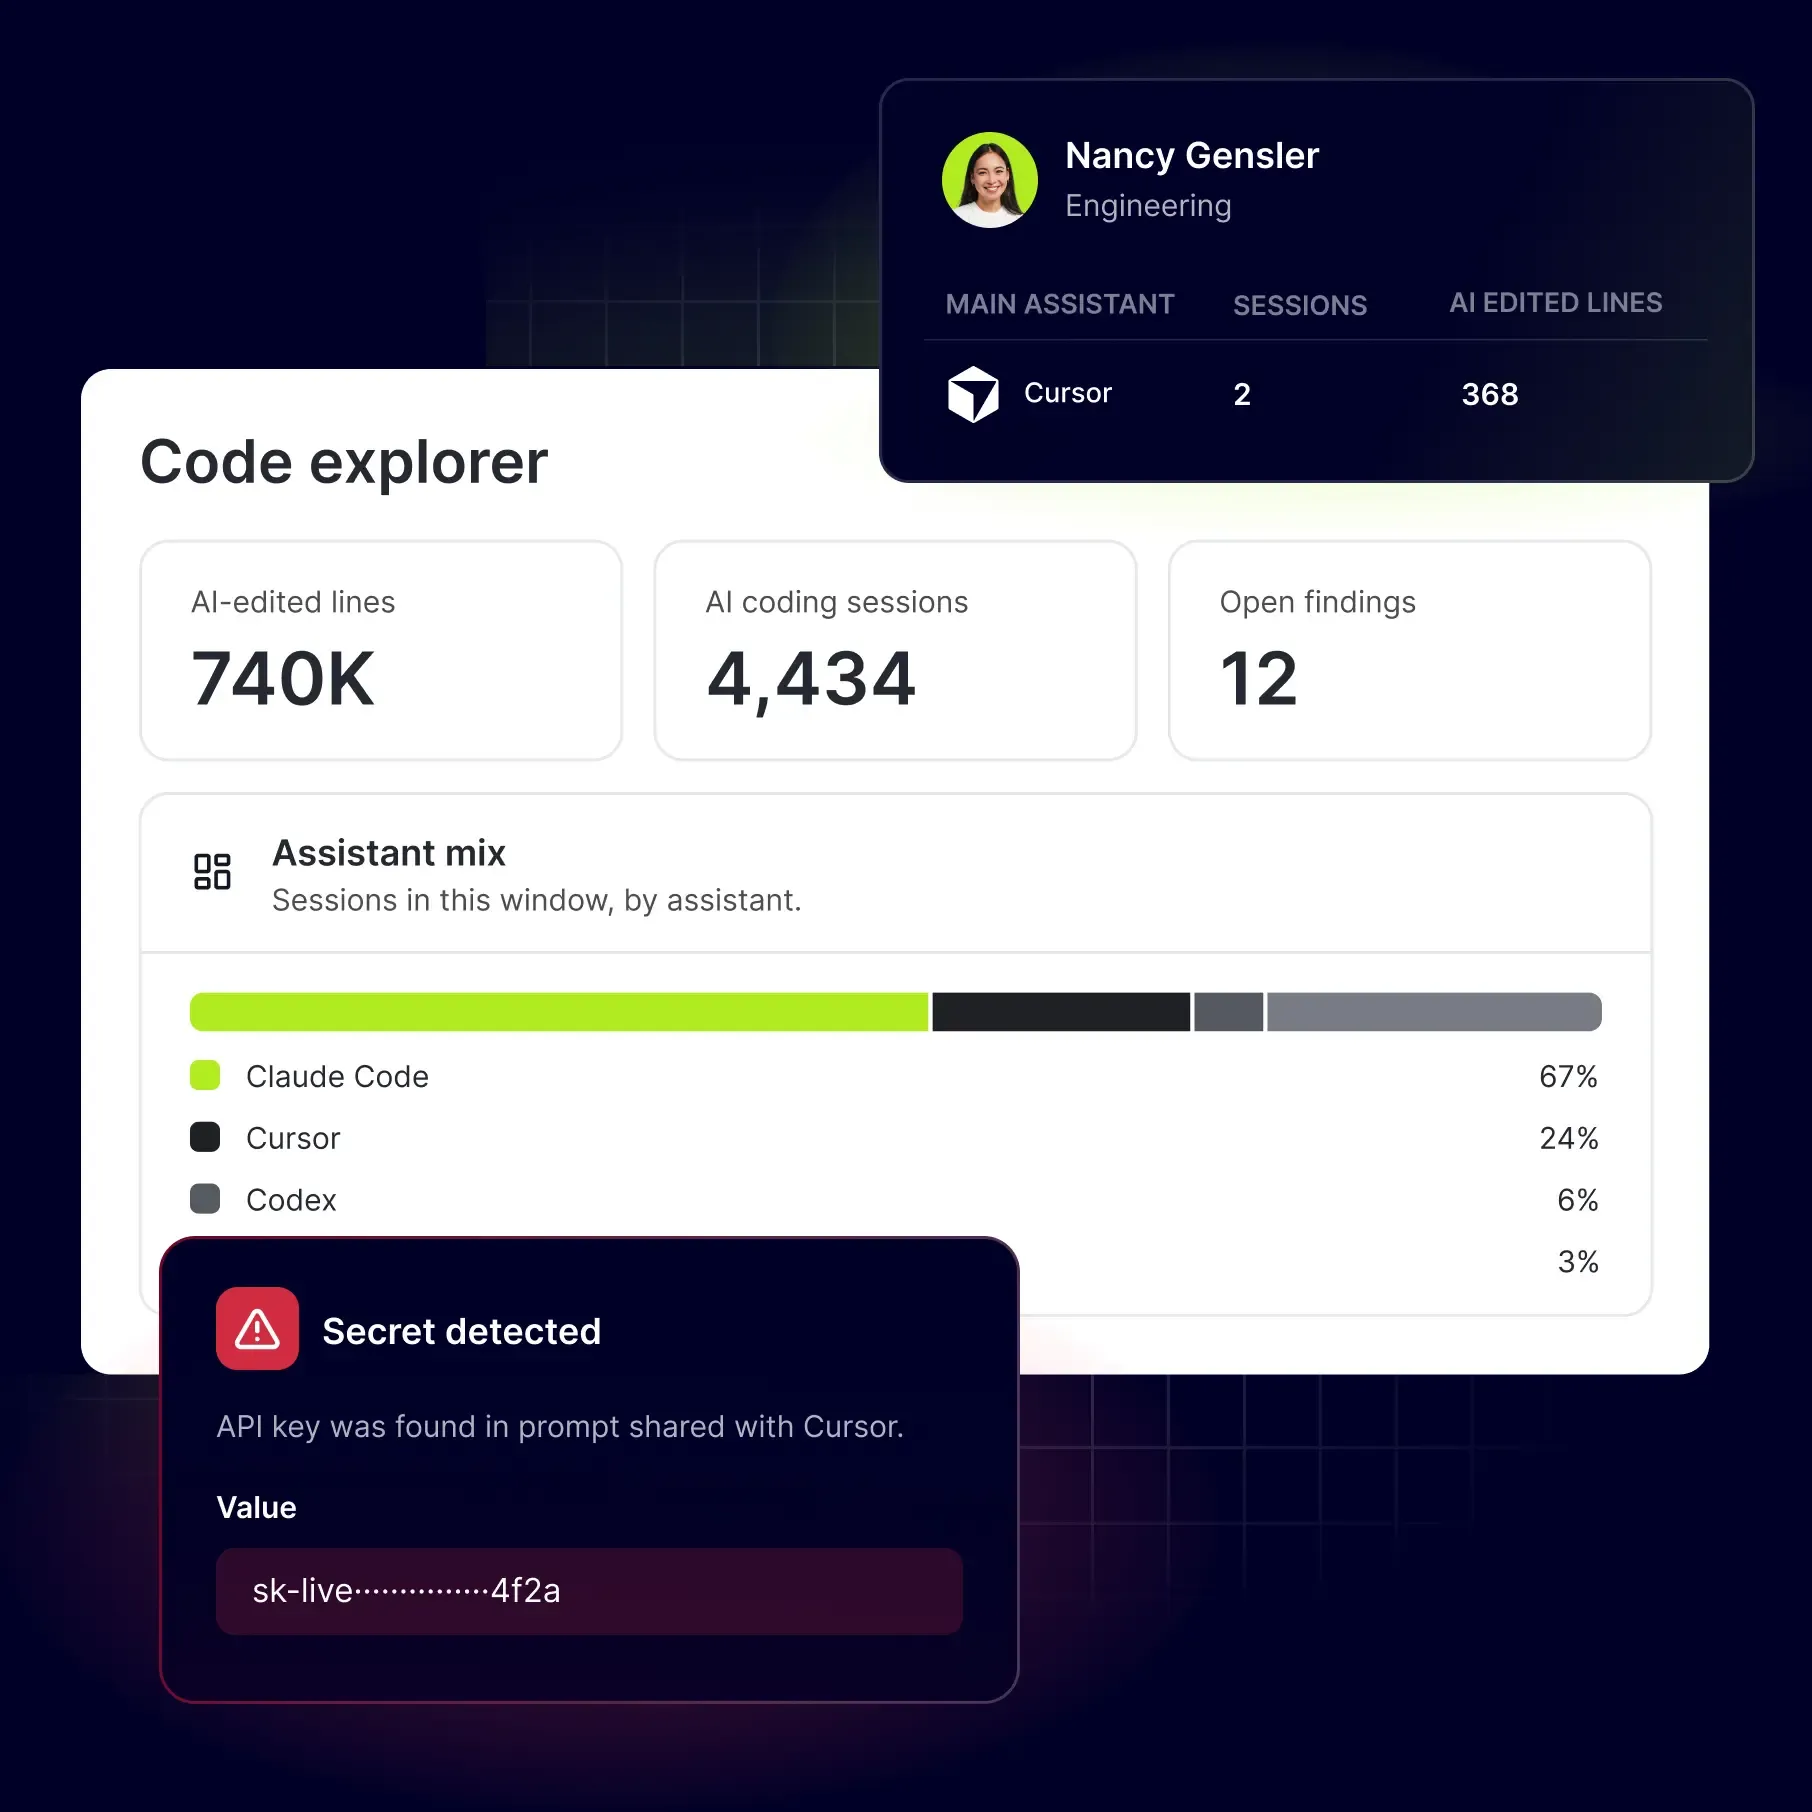
Get full visibility into every coding agent session

Map the agent work to each repository
See which repositories get agent work, how many sessions run in each, and which contributors and assistants are behind them, so you know where AI is shaping your codebase

Measure how much of your code is AI-written
Compare committed lines against assistant output on each device to see the share of AI code, with coverage shown alongside so unmanaged devices don’t skew the number.

Track what each of your agent connects to
Follow all tool calls and MCP servers an agent reaches, with inputs, outputs, and error states, so no external connection goes unaccounted for across your development workflow.

Know which sessions require an urgent review
Identify the sessions that need a human eye first, ranked by findings, risk level, and activity volume, so your team spends review time where it counts instead of reading every log.
HOW IT WORKS
Every AI coding session automatically becomes evidence — for audits, compliance, and accountability
A lightweight desktop sensor runs on each managed developer device, reading AI coding agent activity locally and scanning it on the device as it happens.
- 1
Install the desktop sensor
Roll out NordLayer AI Scout’s lightweight sensor to each managed developer device, where it runs quietly in the background with no change to how developers work or which tools they choose.
- 2
Rebuild each agent session
Dedicated parsers for Claude Code, Cursor, Codex, and more rebuild each session step by step, tying tool calls, files, MCP servers, context, reasoning, and errors to the agent, developer, and repository behind it.
- 3
Flag risk on the device
On-device detection scans the wider agent workflow as it runs, flagging secrets, keys, source code at risk, and unexpected MCP servers or external services so you can identify threats early and respond before they spread.
- 4
Review it in one console
Investigate sessions in one console for web and desktop AI use, with repositories, AI share, and findings ranked by risk and volume so your team knows which sessions to prioritize first.
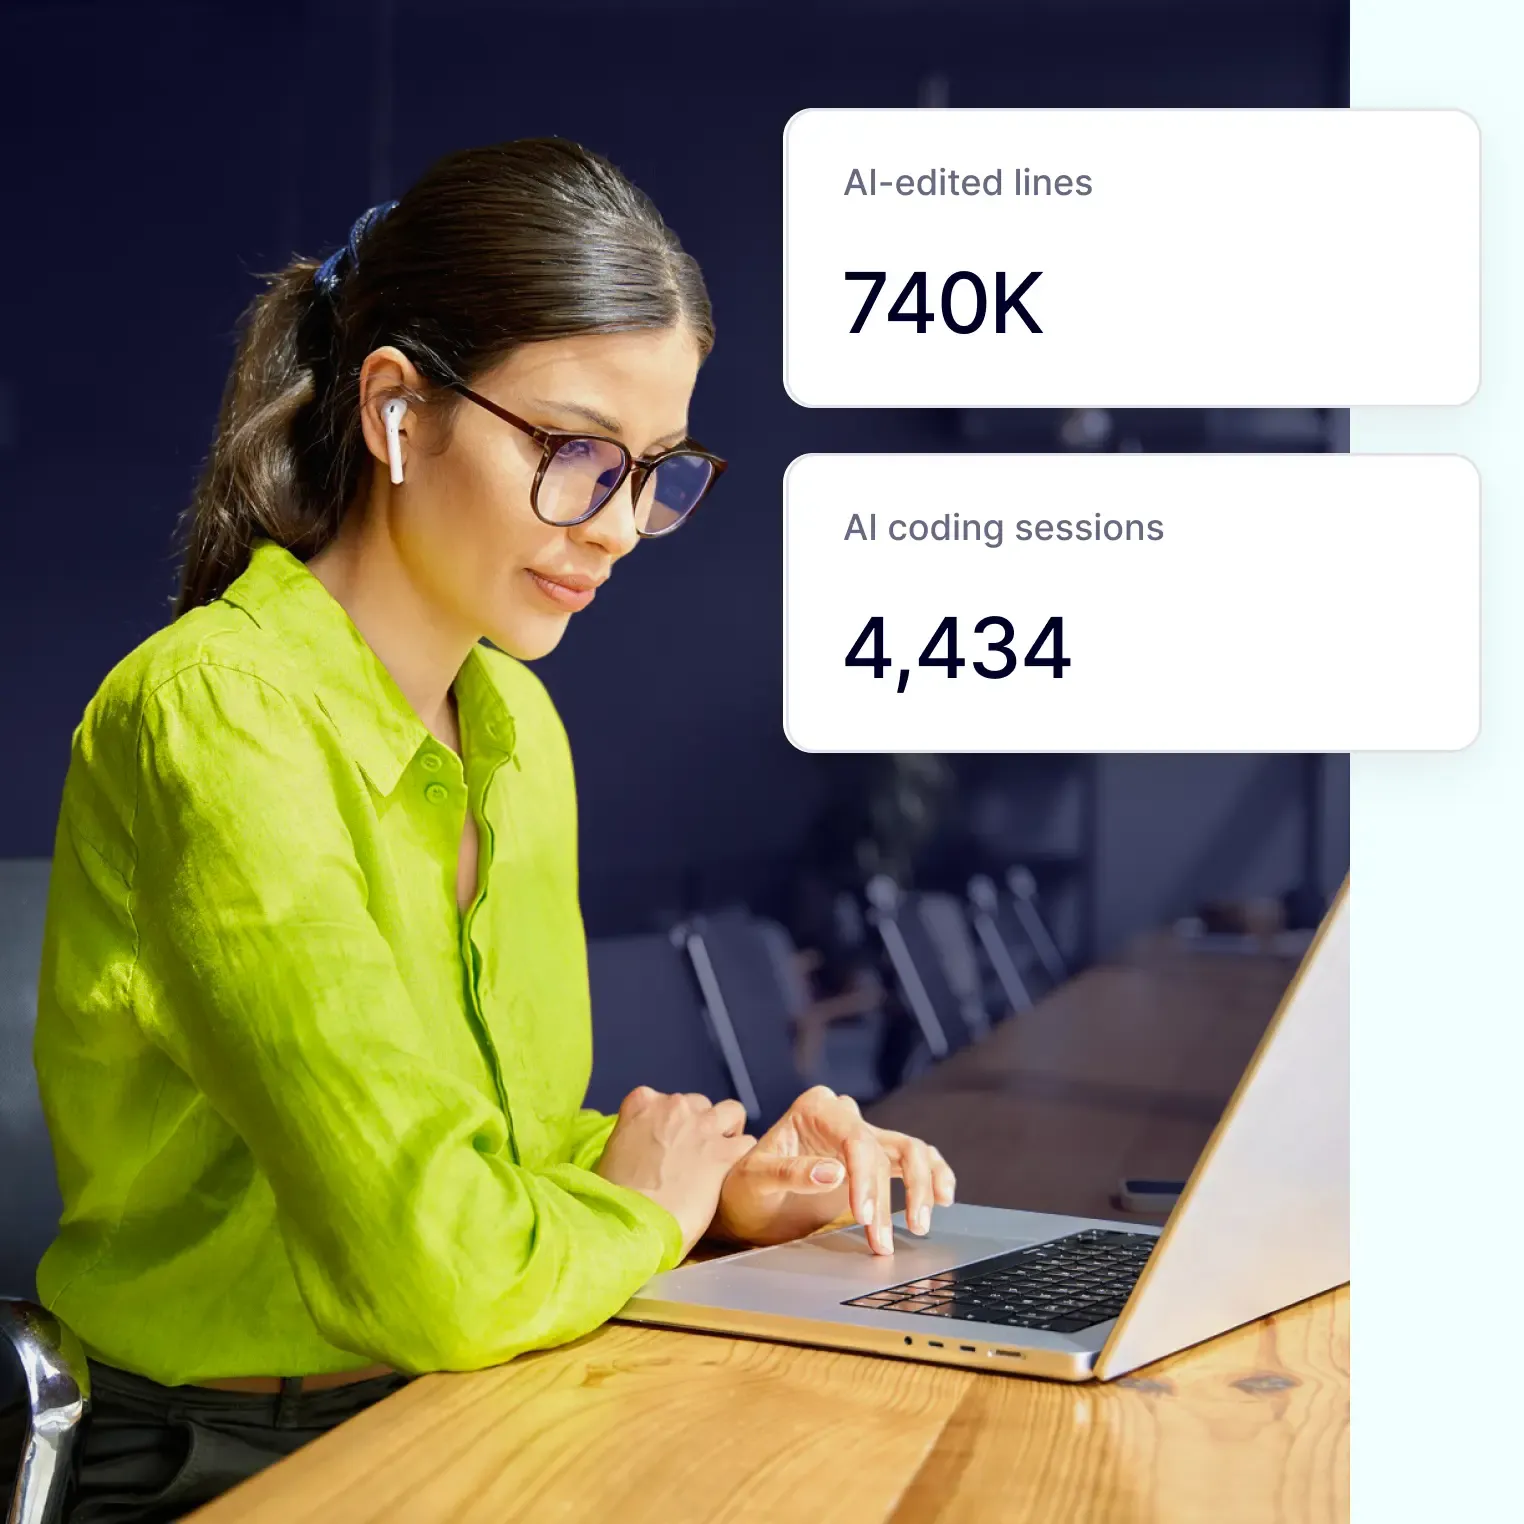
Know exactly what your coding agents did today
See how NordLayer AI Scout turns every agent coding session into a clear record your security and engineering teams can act on.
WHO IT’S FOR
Built for the teams that own AI coding risk

Security teams
Detect sensitive data leaving developer devices, spot risky MCP servers and connections, and bring shadow AI agents into view without slowing anyone down.

Engineering leaders
Measure real AI adoption across teams and repositories, so your tooling and budget decisions are made on data, not assumptions.

Developers
Keep using the AI agents you need while guardrails run quietly in the background and stay out of your workflow.
WHAT IT COVERS
Monitor usage across the AI coding agents your team relies on
NordLayer AI Scout supports Claude Code, Cursor, Codex, and the other coding agents below out of the box, including those running in Docker sandboxes, with no change to developer workflows.
ChatGPT
Claude / Claude Code
Gemini
Copilot
Perplexity
DeepSeek
HuggingFace Chat
Cursor
Antigravity
Codex
Cline
Kilo Code
opencode
Zoo Code
Pi
OpenHands


Spotted your team’s tools? Start securing them today
CUSTOMER REVIEWS
Why teams around the world choose NordLayer
See how organizations use NordLayer to simplify security management, protect access to company resources, and strengthen their defenses against evolving cyber risks.
In Security Service Edge category
NordLayer has been very accommodating in terms of our needs. They are flexible to cater timing of payments and also providing exclusive support
Everything is super efficient and easy: negociations, setup, dashboard, accounting, support
Very easy to set up and use and is very reliable. There are good security options to enable the configuration comply with security policies.
FURTHER READING
Learn more about AI coding agent security
CYBERSECURITY LEARNING CENTER
What is AI agent security?
CYBERSECURITY LEARNING CENTER
What is generative AI security?
CYBERSECURITY LEARNING CENTER
AI security best practices: a guide for enterprises
Additional info
Frequently asked questions
AI coding agents such as Claude Code get the same access as the developer who runs them, but they can be tricked by prompt injection, set up incorrectly, or simply make mistakes. They can also reach passwords, production systems, MCP servers, and outside services much faster than a person would, so one bad step in a coding session can spread before anyone notices.
You compare the code your team commits with the code its agents actually produced. NordLayer AI Scout does this on each managed device and shows the AI-written share next to how many devices it covers, so you know how complete the number is. The sensor compares counts on-device – no source code ever leaves the laptop.
Start by seeing what each agent does, including the tools it uses, the files it opens or changes, and the services it connects to. Then watch for secrets and source code at risk, and review the riskiest sessions first, so your team keeps shipping secure code without losing control.
Track which coding agents your developers use, how many sessions run in each repository, and how much committed code comes from AI. Together, these numbers show where AI is helping your team and where adoption is still low.
Yes. NordLayer AI Scout shows every MCP server a session reached in Claude Code, Cursor, Codex, and other supported agents, along with tool calls, inputs, outputs, and errors. You can then approve servers org-wide or block them for a specific team or role.